Trojaned OpenSSH (in 2002) https://lobste.rs/s/ti42hu #openbsd #security
http://miod.online.fr/software/openbsd/stories/trojan.html
openbsd
Just read a great write-up by @miodvallat on the 2002 OpenSSH trojan incident.
It's a fantastic look at early incident response, code auditing, and how OpenBSD handled one of the first major software supply-chain attacks.
Definitely worth a read:
http://miod.online.fr/software/openbsd/stories/trojan.html
#openbsd #openssh #security
It's a fantastic look at early incident response, code auditing, and how OpenBSD handled one of the first major software supply-chain attacks.
Definitely worth a read:
http://miod.online.fr/software/openbsd/stories/trojan.html
#openbsd #openssh #security
EDIT: the recording is available here: https://exquisite.tube/w/nQbc54t4G7YGaqiryZ7mg1
On 10 March 2021, I had only just fallen asleep when my phone started buzzing. Then another notification, and another. In a matter of minutes, 142 of my servers went up in the clouds. And not the cloud-computing kind.
Most of them were physically going up in a column of smoke in Strasbourg.
My wife looked at me and asked if I wanted a coffee. I nodded. It was going to be a very long day.
At EuroBSDCon 2026, I won't be giving a theoretical lecture on high availability. Instead, I’m going to tell the raw story of that night: the emergency recovery, the architectural choices that actually saved us, and the ones that crumbled under pressure (because we rarely talk about what fails).
Most of all, I’ll explain why that night changed my perspective, and why I’ve come to see BSD systems not just as operating systems, but as essential, practical tools for building simpler, more resilient infrastructure.
The official schedule is now live. If you want to hear a real-world post-mortem, join me on Saturday, 12 Sept at 11:15 (Room D.0.02).
EuroBSDCon Full schedule: https://events.eurobsdcon.org/2026/schedule/
See you there! ☕️
#FreeBSD #NetBSD #OpenBSD #DragonFlyBSD #RunBSD #EuroBSDCon #SysAdmin #SelfHosted #IT #EuroBSDCon2026 #BSDCon
Edited 59d ago

OpenBSD through 7.9 has a use-after-free allowing local privilege escalation to root (CVE-2026-57589) https://lobste.rs/s/7hmu0w #openbsd #security
https://nvd.nist.gov/vuln/detail/cve-2026-57589
Hey people,
I recently graduated from my #SysAdmin apprenticeship and I am looking for an entry position in the field of #Linux/ #Networking Administration/Engineering or #DevOps in #NRW, #Germany (ideally around #Düsseldorf), or Remote.
As part of the apprenticeship I conducted an internship at a Neuroscience Institute of Research Centre Juelich, where I accomplished my project of automating #OpenBSD routers using #pyinfra #GitOps.
1/2
Boosts appreciated 🙏🏻
Edited 124d ago

also what do you use to navigate your photos and videos on #openbsd?

@BoxyBSD Returns to #FreeBSD: Migrating from #Proxmox to #Sylve (#bhyve)
Some journeys don't end where you expect them to. Sometimes they bring you right back to where everything began, only with a lot more experience and a much better ecosystem waiting for you.
That's exactly what is happening with BoxyBSD!
In my (longer) blog post I cover my circuit, where I moved from bhyve to Proxmox, developed many tools for Proxmox and now moved back to FreeBSD with bhyve and Sylve.
More details in my blog post: https://gyptazy.com/blog/boxybsd-moving-from-proxmox-to-bhyve-with-sylve/
#RUNBSD #bsd #freebsd #boxybsd #openbsd #netbsd #sylve #bhyve #opensource #vps #vpshosting #opensource #community #bsdcafe #boxybsd
Some journeys don't end where you expect them to. Sometimes they bring you right back to where everything began, only with a lot more experience and a much better ecosystem waiting for you.
That's exactly what is happening with BoxyBSD!
In my (longer) blog post I cover my circuit, where I moved from bhyve to Proxmox, developed many tools for Proxmox and now moved back to FreeBSD with bhyve and Sylve.
More details in my blog post: https://gyptazy.com/blog/boxybsd-moving-from-proxmox-to-bhyve-with-sylve/
#RUNBSD #bsd #freebsd #boxybsd #openbsd #netbsd #sylve #bhyve #opensource #vps #vpshosting #opensource #community #bsdcafe #boxybsd
Edited 113d ago
Still playing about with #CoW aka #fvwm on #Wayland and I'm finding / reporting some bugs but I'm still not sure how I feel about stacking window managers?
Who here still uses fvwm and why?
Even better share with us your fvwm desktop screenshots.
https://codeberg.org/thomasadam/cow
#WindowManager #Linux #OpenBSD #FreeBSD
Who here still uses fvwm and why?
Even better share with us your fvwm desktop screenshots.
https://codeberg.org/thomasadam/cow
#WindowManager #Linux #OpenBSD #FreeBSD
Edited 108d ago
Things are probably still propagating over to the new server, but I am officially hosting my blog locally via #OpenBSD on my HP T630
Wrote about setting up the process here:
"Setup a Simple, Self-Hosted Web Server with OpenBSD"
https://btxx.org/posts/self-hosted-openbsd/
(I also have some basic details on my infrastructure page https://btxx.org/infra/)

RE: https://floss.social/@doctormo/116927739358578223
So serious question...
What is #OpenBSD's take on AI? (in general and as a whole, i imagine individual contributors have their own stances of course).
I'm running out of places to run to (and I'm already standing and fighting as much as I am able).
Migrating from Codeberg Pages to an OpenBSD VPS by @nemin https://lobste.rs/s/4wh5ng #openbsd #web
https://nemin.hu/vps/index.html
GEFS: The File Shredder of the Future https://lobste.rs/s/vxkb8z #video #openbsd #osdev
https://exquisite.tube/w/3QQimMdswWJxrsPaJtak2u
This might be interesting for people running old computers and by various
reasons do not use corporate web browsers. Of course if you use simple web
browser like #Dillo, #Links2, #Lynx, #w3m and any other, you may still want to block
connections with 3rd party sites. If you run #OpenBSD or #NetBSD then you have
few options:
(1) Use PiHole, Blocky, Gravastar - but this will not help if you are out of
home.
(2) Use unwind - if you are running OpenBSD.
(3) Use hblock or tblock.
Hblock and tblock are bash/python scripts which update /etc/hosts file using
blocklists available in the Internet. Hblock depends only on bash, so it will
work after some tweaks even on OS/2. Tblock depends on python and few its
modules, so on BSDs it needs manual installation, but it is a little more
user-friendly. Refer to: https://github.com/hectorm/hblock and
https://codeberg.org/tblock/tblock for more information! Remember: running
tblock in aggresive mode on Atom N210 will drain computing powers
enough to block your Internet conenction totally.
reasons do not use corporate web browsers. Of course if you use simple web
browser like #Dillo, #Links2, #Lynx, #w3m and any other, you may still want to block
connections with 3rd party sites. If you run #OpenBSD or #NetBSD then you have
few options:
(1) Use PiHole, Blocky, Gravastar - but this will not help if you are out of
home.
(2) Use unwind - if you are running OpenBSD.
(3) Use hblock or tblock.
Hblock and tblock are bash/python scripts which update /etc/hosts file using
blocklists available in the Internet. Hblock depends only on bash, so it will
work after some tweaks even on OS/2. Tblock depends on python and few its
modules, so on BSDs it needs manual installation, but it is a little more
user-friendly. Refer to: https://github.com/hectorm/hblock and
https://codeberg.org/tblock/tblock for more information! Remember: running
tblock in aggresive mode on Atom N210 will drain computing powers
enough to block your Internet conenction totally.
Cleaning costs, or, examining the OpenBSD -fret-clean flag https://lobste.rs/s/z5v07a #openbsd
https://briancallahan.net/blog/20260811.html
Setup a Simple, Self-Hosted Web Server with OpenBSD https://lobste.rs/s/nfcclq #openbsd #web
https://btxx.org/posts/self-hosted-openbsd/
Repeating Ourselves Less with M4 https://lobste.rs/s/uueocw #openbsd #unix
https://nemin.hu/httpd-macros/index.html
My new desktop wallpaper on my #OpenBSD and #Fedora systems. This is where I really want to be.
🏕️ 🛶 
#ShowYourDesktop #ShareYourDesktop #Screenshots #DesktopScreenshots


I've been trying to explore the world outside GNU/Linux (or, as I've recently taken to calling it, "Sexual predator userspace plus egotistical botlicker kernel"). Naturally, the first stop on this road is the fragmented world of #BSD.
I won't lie, the experience is very reminiscent of running Linux in the 1990s: hardware support is dicey at best, it's very rare to find commercial software that will run on it, and the guiding philosophy seems to be that user-friendliness is an undesirable quality that will only result in The Wrong People using your software. Nevertheless, I'm committed to giving it a fair trial.
So far my favorite variant is #OpenBSD, especially for servers. I like the fact that it's secure by default, rather than being a hacker's dream out of the box that you then have to figure out how to secure. But I have questions.
- One of the #FreeBSD features I've heard touted a lot is "jails," which I gather means "like Docker but harder to use". But this doesn't seem to be a feature in OpenBSD. Is there something equivalent in the OpenBSD world, perhaps under another name?
- The only *BSD that I know for sure has banned LLM contributions is #NetBSD. What, if any, are the LLM policies of OpenBSD and FreeBSD?
- Has anybody tried audio production in BSD? What's the experience like? It took years for Linux to get to the point where you could more or less do serious audio work, and I hate to think of regressing back to "if you buy this one particular sound card they stopped making in 1998 and recompile the kernel with a dodgy patch someone posted to USENET you can maybe kind of play a .WAV file".
Thanks in advance for your help!
(I have been informed by an anonymous source that "BSD jails" are in fact what they put you in if you use the software without a valid BSD license. I am not sure this is correct.)
how many people run #openbsd here?
like = you run it on server
boost = you run it on desktop/laptop :)
❤️
like = you run it on server
boost = you run it on desktop/laptop :)
❤️
Dead Software Walking: The ongoing evolution of relayd(8) and httpd(8) https://lobste.rs/s/i6e5wp #openbsd #practices
https://rsadowski.de/posts/2026/dead-software-walking-relayd-and-httpd/
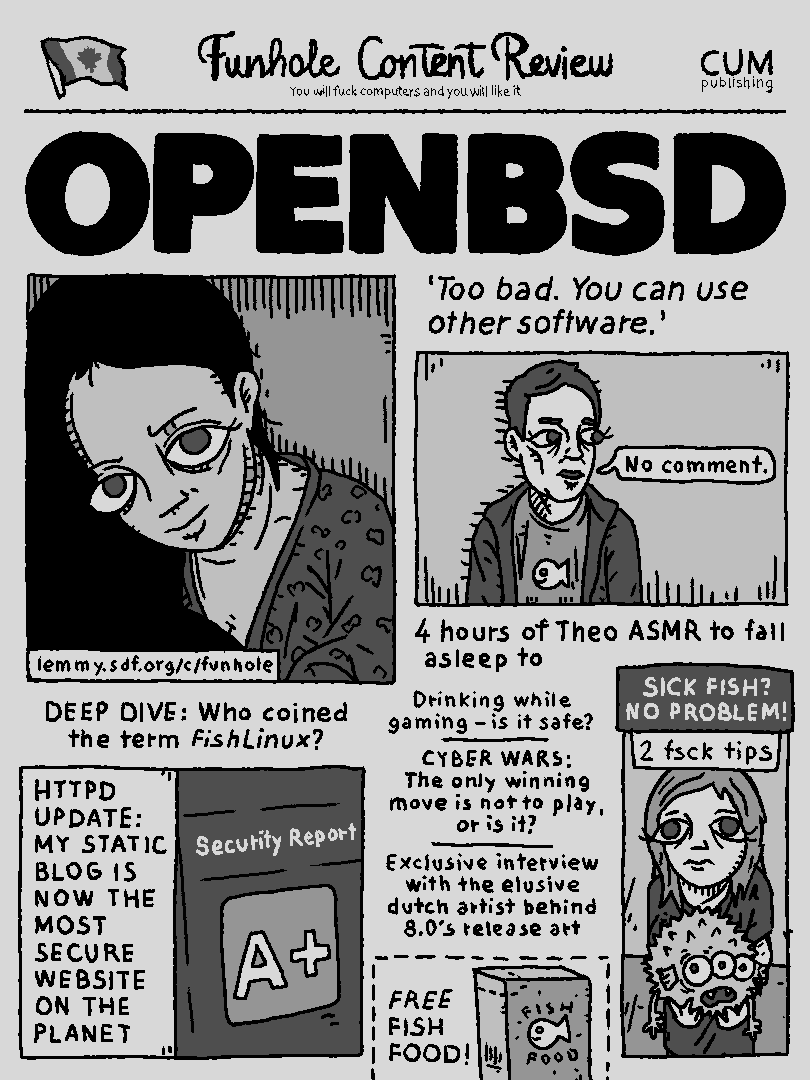
DUST VICTIMS PRAY FOR OKLAHOMA RAIN
#content_review #openbsd #unix_surrealism #comic #art #fediart #ai #programming #runbsd