A thing I love about the EUVD is that it doesn't bombard you with consent prompts and tracking cookies... as one expects from a "vulnerability database" https://euvd.enisa.europa.eu
cve

Register now for “CVE/FIRST VulnCon 2026” on April 13–16, 2026!!!
In-person & virtual available: https://www.first.org/conference/vulncon26/registration
#CVE #FIRST #VulnCon26 #VulnerabilityManagement #Vulnerability

I think a LOT of people are missing the fact that we got LUCKY with this malicious backdoor.
The backdoor was created by an Insider Threat - by a developer / maintainer of various linux packages. The backdoor was apparently pushed back on March 8th (I believe) and MADE IT PAST all QA checks.
Let me state that again. Any quality assurance, security checks, etc., failed to catch this.
This was so far upstream, it had already gotten into the major Linux distributions. It made it into Debian pre-release, Fedora rolling, OpenSUSE rolling, Kali rolling, etc.
This is an example of Supply Chain Security that CISOs love to talk and freak out about. This is an example of an Insider Threat that is the boogey man of corporate infosec.
A couple more weeks, and it would have been in many major distributions without any of us knowing about it.
The ONLY reason we know about it is because @AndresFreundTec got curious about login issues and some benchmarking checks that had nothing to do with security and ran the issue down and stumbled upon a nasty mess that was trying to remain hidden.
It was luck.
That's it. We got lucky this time.
So this begs the question. Did the malicious insider backdoor anything else? Are they working with anyone else who might have access to other upstream packages? If the QA checks failed to find this specific backdoor by this specific malicious actor, what other intentional backdoors have they missed?
And before anyone goes and blames Linux (as a platform or as a concept), if this had happened (if it HAS happened!!!) in Windows, Apple, iOS, etc.... we would not (or will not) know about it. It was only because all these systems are open source that Andres was able to go back and look through the code himself.
Massive props and kudos and all the thank yours to Andres, those who helped him, to all the Linux teams jumping on this to fix it, and to all the folks on high alert just before this Easter weekend.
I imagine (hope) that once this gets cleaned up, there will be many fruitful discussions around why this passed all checks and what can be changed to prevent it from happening again.
(I also hope they run down any and all packages this person had the signing key for....)

Tic-TAC aka CVE-2024-42845, a Remote Code Execution vulnerability inside Open Source Medical Tools when a new DICOM file is imported.
Deetz: https://www.partywave.site/show/research/Tic%20TAC%20-%20Beware%20of%20your%20scan
@CVE_Program @vxunderground @itsfoss #dicom #cve @defcon


We released the #XLibre Xserver 25.0.0.22 and 25.1.4 on Apr 21 containing #security fixes for CVE-2026-33999, CVE-2026-34000, CVE-2026-34001, CVE-2026-34002, and CVE-2026-34003 of the X.Org Server. We recommend everyone update ASAP. #CVE https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.1.4
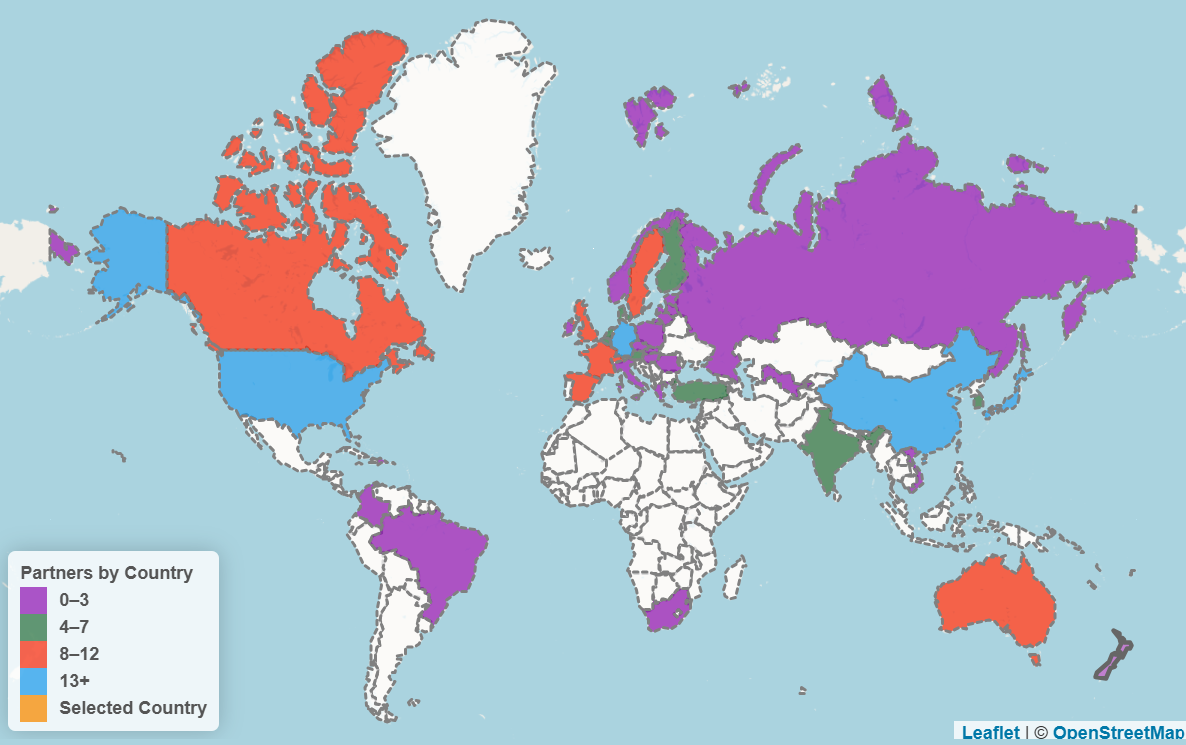
500+ Organizations Now Participating as CVE Numbering Authorities (CNAs)!
As of March 31, 2026, there are 502 CNAs (499 CNAs and 3 CNA-LRs) from 42 countries participating in the CVE Program
Learn more:
https://www.cve.org/Media/News/item/blog/2026/03/31/502-Organizations-Participating-as-CNAs
#cve #cna #vulnerability #vulnerabilitymanagement #informationsecurity #infosec #cybersecurity
2026-05-20 FreeBSD errata notice and seven security advisories
https://www.reddit.com/r/freebsd/comments/1tjaceg/20260520_freebsd_errata_notice_and_seven_security/
– an overview, including clickable links to CVE records.
Edited 172d ago
We released the #XLibre Xserver 25.0.0.25, 25.1.9, and beta 25.2.2 during the last 4 days containing #security fixes for #CVE-2026-55999 and CVE-2026-56000. We recommend everyone update ASAP.
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.0.0.25
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.1.9
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.2.2
📣 Announcing the immediate availability of:
- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12
‼️ These address the following critical security issues:
- Remote Code Execution via Out of Memory corruption (CVE-2026-109618)
- Remote Code Execution via Stale Global State (CVE-2026-109619)
📝 https://www.php.net/ChangeLog-8.php
🎁 https://www.php.net/downloads?source=Y Windows: https://www.php.net/downloads.php?os=windows
Read more: https://www.php.net/archive/2026.php#2026-10-21-5
The LG TV network scanning story breaking today includes UDP 9999 Kasa discovery broadcasts every 25 seconds. That's the exact port I documented in CVE-2026-13230 as returning unauthenticated precise GPS coordinates from Kasa cameras with no authentication. Any LG TV + unpatched Kasa camera on the same network = GPS harvesting every 25 seconds. @briankrebs Advisory: https://github.com/BadChemical/IoT-Vulnerability-Research-Public/blob/main/TP-Link_Kasa_EC71/Kasa_EC71.md
Edited 63d ago
PHP2Shell: Analyse der kritischen RCE-Schwachstellen (CVE-2026-109618 und CVE-2026-109619)
“Das PHP-Projekt hat am 21. Oktober 2026 außerplanmäßige Sicherheitsupdates veröffentlicht, um zwei kritische Schwachstellen auf Interpreter-Ebene zu s...”
We released the #XLibre Xserver 25.0.0.26, 25.1.11, and beta 25.2.3 in the last few days with fixes for #CVE-2026-88812, 93515 through 93524, 93536, and more. We recommend everyone update ASAP.
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.0.0.26
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.1.11
https://github.com/X11Libre/xserver/releases/tag/xlibre-xserver-25.2.3
Stellungnahme unseres Teams: Das Penzberg-Audit, unsere Fehler und 28 unumstößliche Fakten
“Wir haben die externe, forensische Tiefenprüfung (Deep Audit) unseres ursprünglichen 64-seitigen Sicherheitsberichts zur IT-Infrastruktur der Stadt Pe...”
Another day, another critical vulnerability in an edge device. We’ve analysed the CVE-2026-88771, one of the many vulnerabilities disclosed by Citrix recently, based on observed exploitation attempts, and set out what we learned and key takeaways. 🔍🔒
If you’re managing Citrix infrastructure, now’s the time to check for compromise!
https://www.cert.europa.eu/blog/taking-execute-logging-a-bit-too-literally-cve-2026-88771
#cybersecurity #cve-2026-88771 #vulnerability

Every panel I go on: "Gina but isn't open source inherently less secure than closed source?"
Meanwhile, MS Paint does remote code execution now 💀
https://www.techzine.eu/news/security/145581/paint-vulnerability-allows-rce-patch-is-hard-to-find/
Edited 4d ago
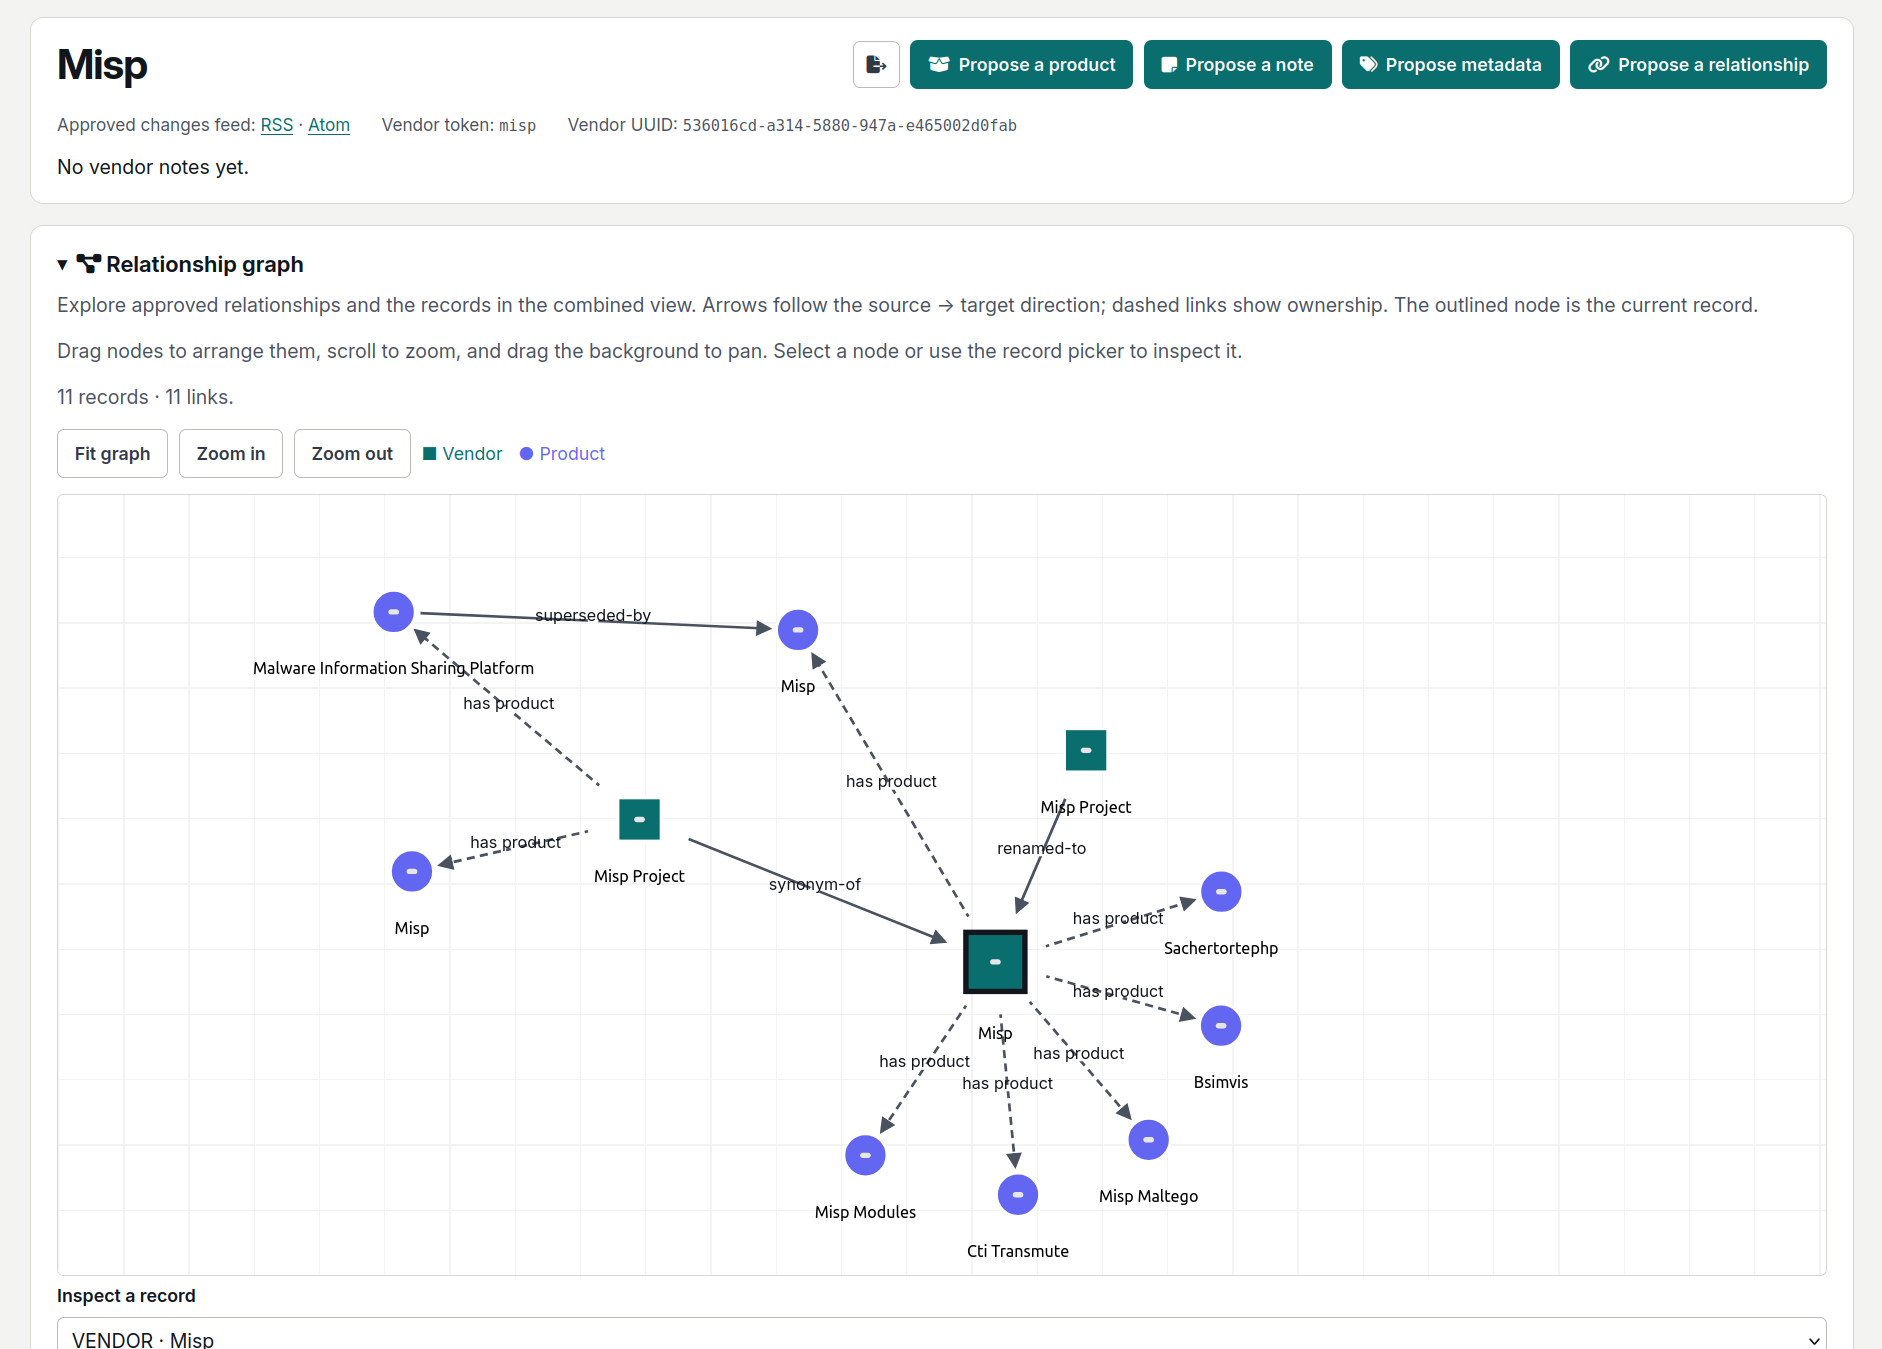
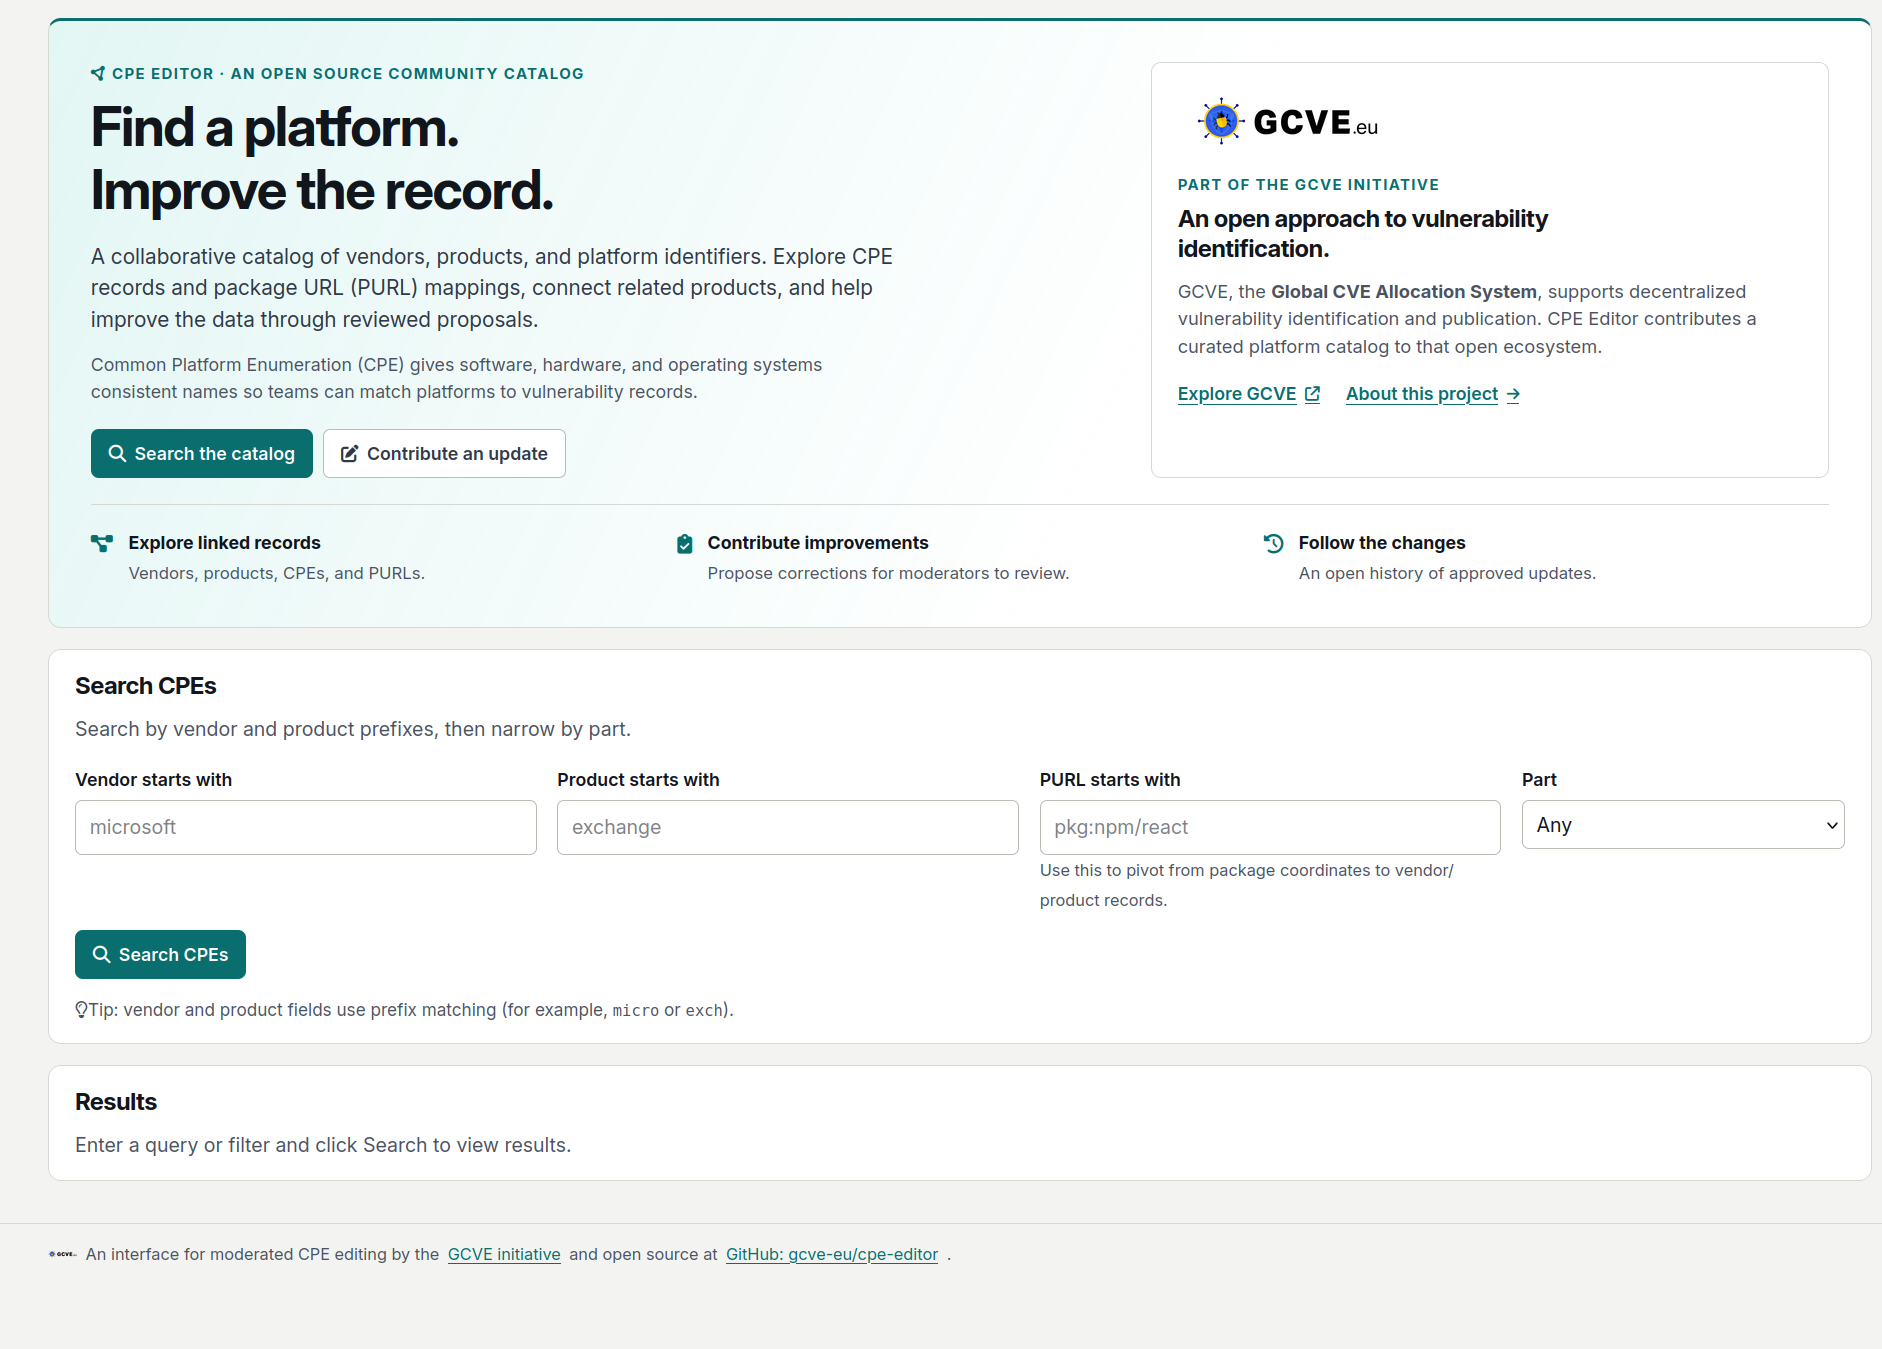
CPE Editor · An open source community catalog - Find a platform. Improve the record.
A collaborative catalog of vendors, products, and platform identifiers. Explore CPE records and package URL (PURL) mappings, connect related products, and help improve the data through reviewed proposals.
A new version has been released including graph view, improved UI and interface and many bugs fixed.
#cpe #cve #vulnerabilitymanagement #vulnerability #cybersecurity #opensource