security mitigations ansible role https://lobste.rs/s/f4alia #devops #security
https://git.sig-io.nl/sigio/mitigations
security
Mini Shai-Hulud - TanStack and more npm packages compromised, with SLSA Build Level 3 provenance attestations https://lobste.rs/s/y1k2qm #security
https://www.stepsecurity.io/blog/mini-shai-hulud-is-back-a-self-spreading-supply-chain-attack-hits-the-npm-ecosystem
Does anyone have recommendations for a Mastodon fork that doesn't require visitors to enable JavaScript to view basic content? The JavaScript dependency is a security risk and user hostile. Visitors should not be required to enable JavaScript when simply visiting a Mastodon server. Plus, the recommendation to use a native app doesn't even work for all Mastodon/ActivityPub instances.
Also, the requirement for JavaScript makes the Mastodon development team seem incompetent. They can't even make a basic web site that doesn't require JavaScript. I could do that when I was in middle school.
>To use the Mastodon web application, please enable JavaScript. Alternatively, try one of the native apps for Mastodon for your platform.

A 0-click exploit chain for the Pixel 10: When a Door Closes, a Window Opens via @refi64 https://lobste.rs/s/l9uweb #android #security
https://projectzero.google/2026/05/pixel-10-exploit.html
You finally patched your infra for the weekend after all the sh*tty things? Well… let’s break out of qemu based guests:
https://github.com/v12-security/pocs/tree/main/qemu
The worst thing, people are providing pocs before maintainers and upstreams have time to fix.
#qemu #kvm #kubevirt #security #vm #kvm
https://github.com/v12-security/pocs/tree/main/qemu
The worst thing, people are providing pocs before maintainers and upstreams have time to fix.
#qemu #kvm #kubevirt #security #vm #kvm
Edited 179d ago
score by collisions, patch by panic https://lobste.rs/s/pi9gjl #practices #security
https://blog.himanshuanand.com/2026/05/score-by-collisions-patch-by-panic/
CVE-2026-40369: Arbitrary Kernel Address Increment via NtQuerySystemInformation https://lobste.rs/s/lwtmzl #security #windows
https://github.com/orinimron123/CVE-2026-40369-EXPLOIT
Cheap smart doorbell allows fleet-wide account takeover and call hijacking by @ABGEO https://lobste.rs/s/yxj57x #hardware #reversing #security
https://www.abgeo.dev/blog/anyone-can-ring-your-doorbell/
Recent Kernel exploits, attack surface reduction, example IPSEC by @hanno https://lobste.rs/s/kep6ok #linux #networking #security
https://www.openwall.com/lists/oss-security/2026/05/16/3
Gradient ascent is superior to generate-and-test in any domain in which you have even a heuristic gradient that is sometimes wrong.
Why people working on software where something serious is at stake would throw out known gradient to use a code generator + testing is beyond my capacity to understand.
https://1password.social/@1password/116580082041363054
#AI #GenAI #GenerativeAI #LLM #VibeCoding #Software #SoftwareDevelopment #tech #dev #security #InfoSec #PasswordManagers
Why people working on software where something serious is at stake would throw out known gradient to use a code generator + testing is beyond my capacity to understand.
https://1password.social/@1password/116580082041363054
#AI #GenAI #GenerativeAI #LLM #VibeCoding #Software #SoftwareDevelopment #tech #dev #security #InfoSec #PasswordManagers
Security is Hard, Y’all https://lobste.rs/s/qoptbx #security
https://textslashplain.com/2026/08/04/security-is-hard-yall/
Debian SE Linux and PinTheft https://lobste.rs/s/jlhsqw #linux #security
https://etbe.coker.com.au/2026/05/24/debian-selinux-pintheft/
2026-05-20 FreeBSD errata notice and seven security advisories
https://www.reddit.com/r/freebsd/comments/1tjaceg/20260520_freebsd_errata_notice_and_seven_security/
– an overview, including clickable links to CVE records.
Edited 173d ago
#Trump admin plans to withhold homeland #security #funding to force #states into #election changes
The Trump admin is threatening to withhold tens of millions of dollars in federal homeland security funds from states unless they adopt a sweeping set of election changes, according to multiple sources & internal documents obtained by CNN.
#law #US #Constitution #VotingRights #TrumpCoup #midterms #BigLie #MafiaState #WhiteSupremacy
https://www.cnn.com/2026/06/22/politics/homeland-security-grants-election-changes?cid=ios_app
Edited 142d ago

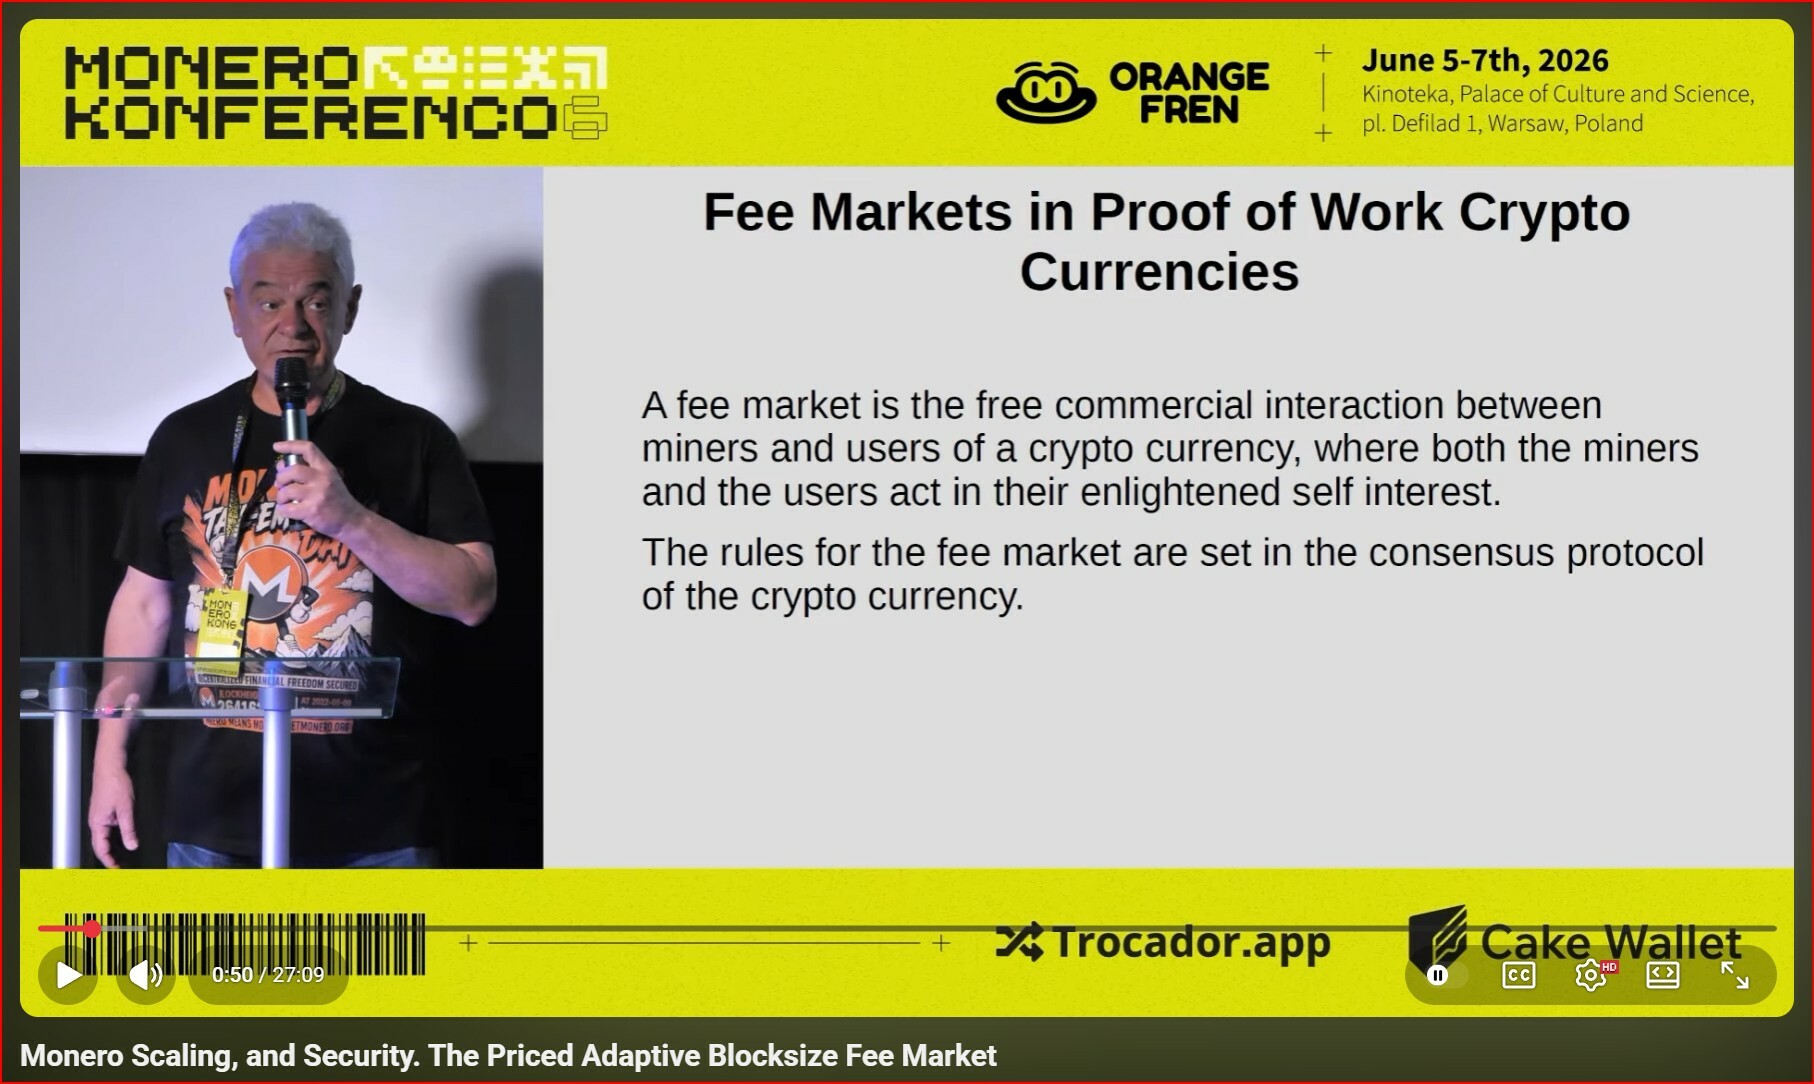
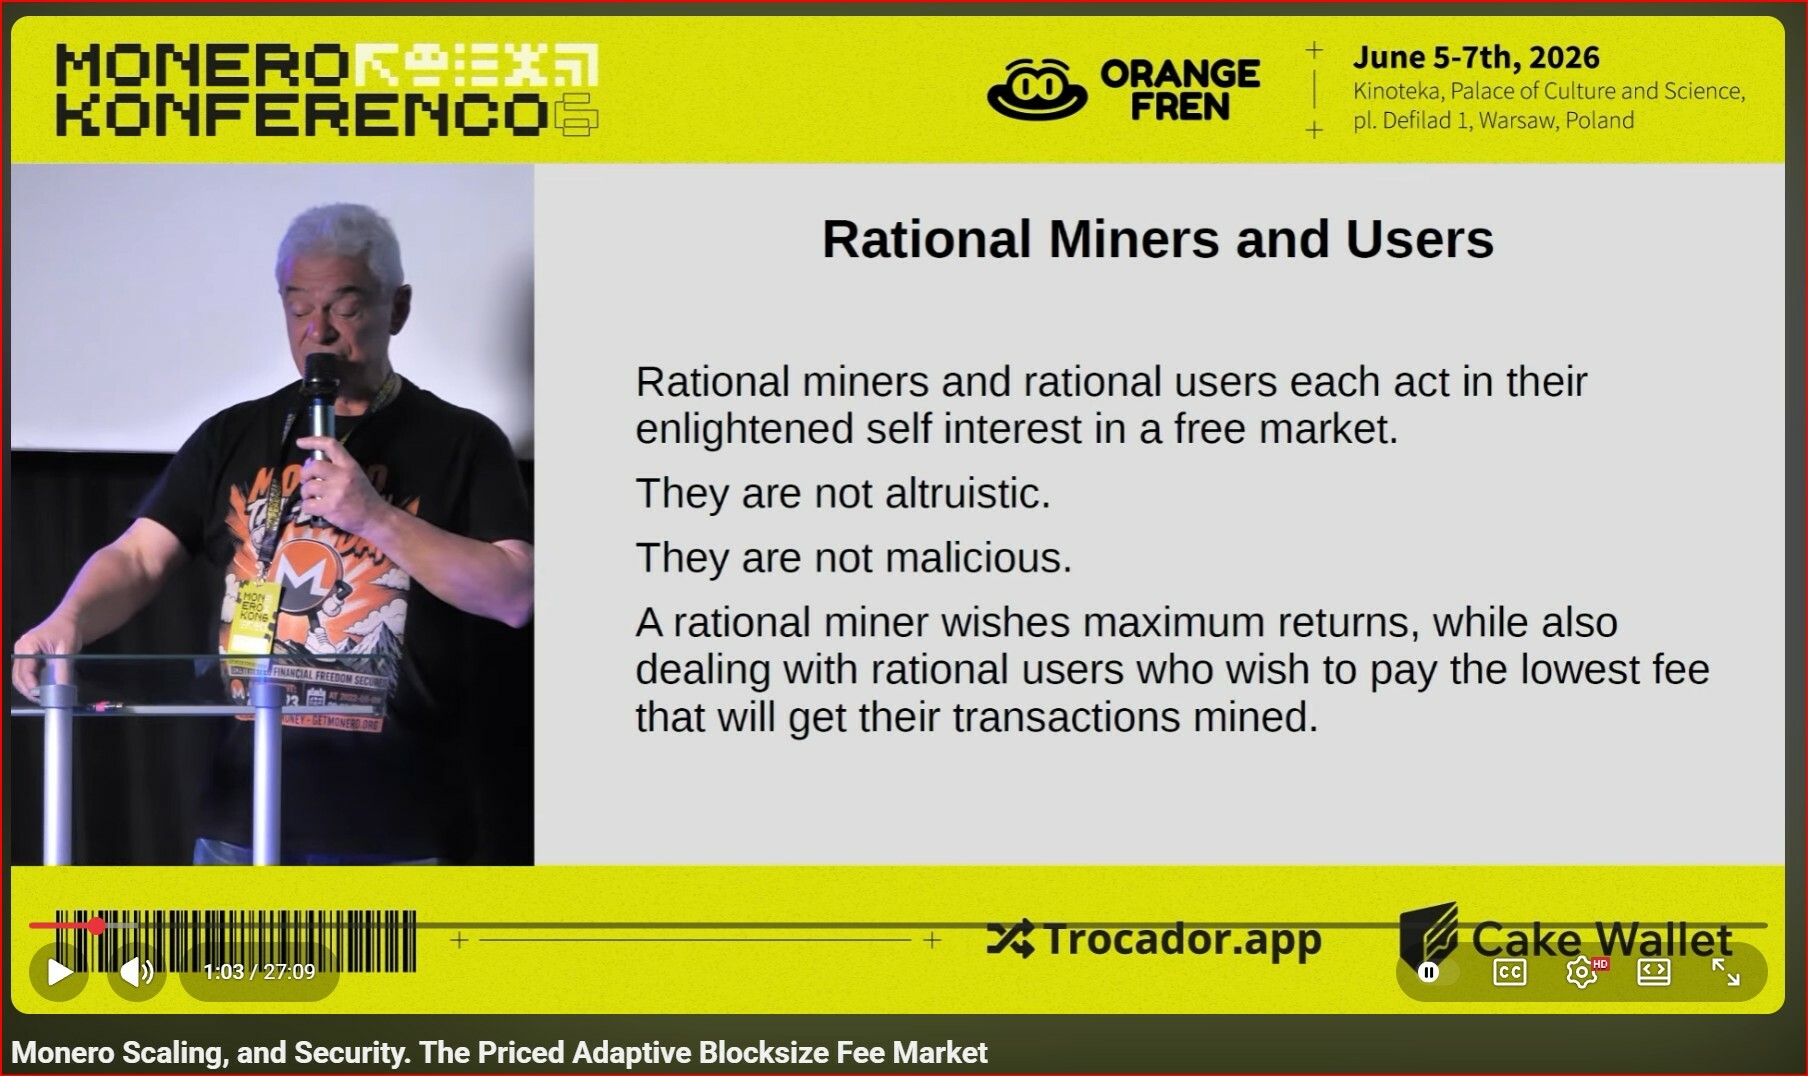
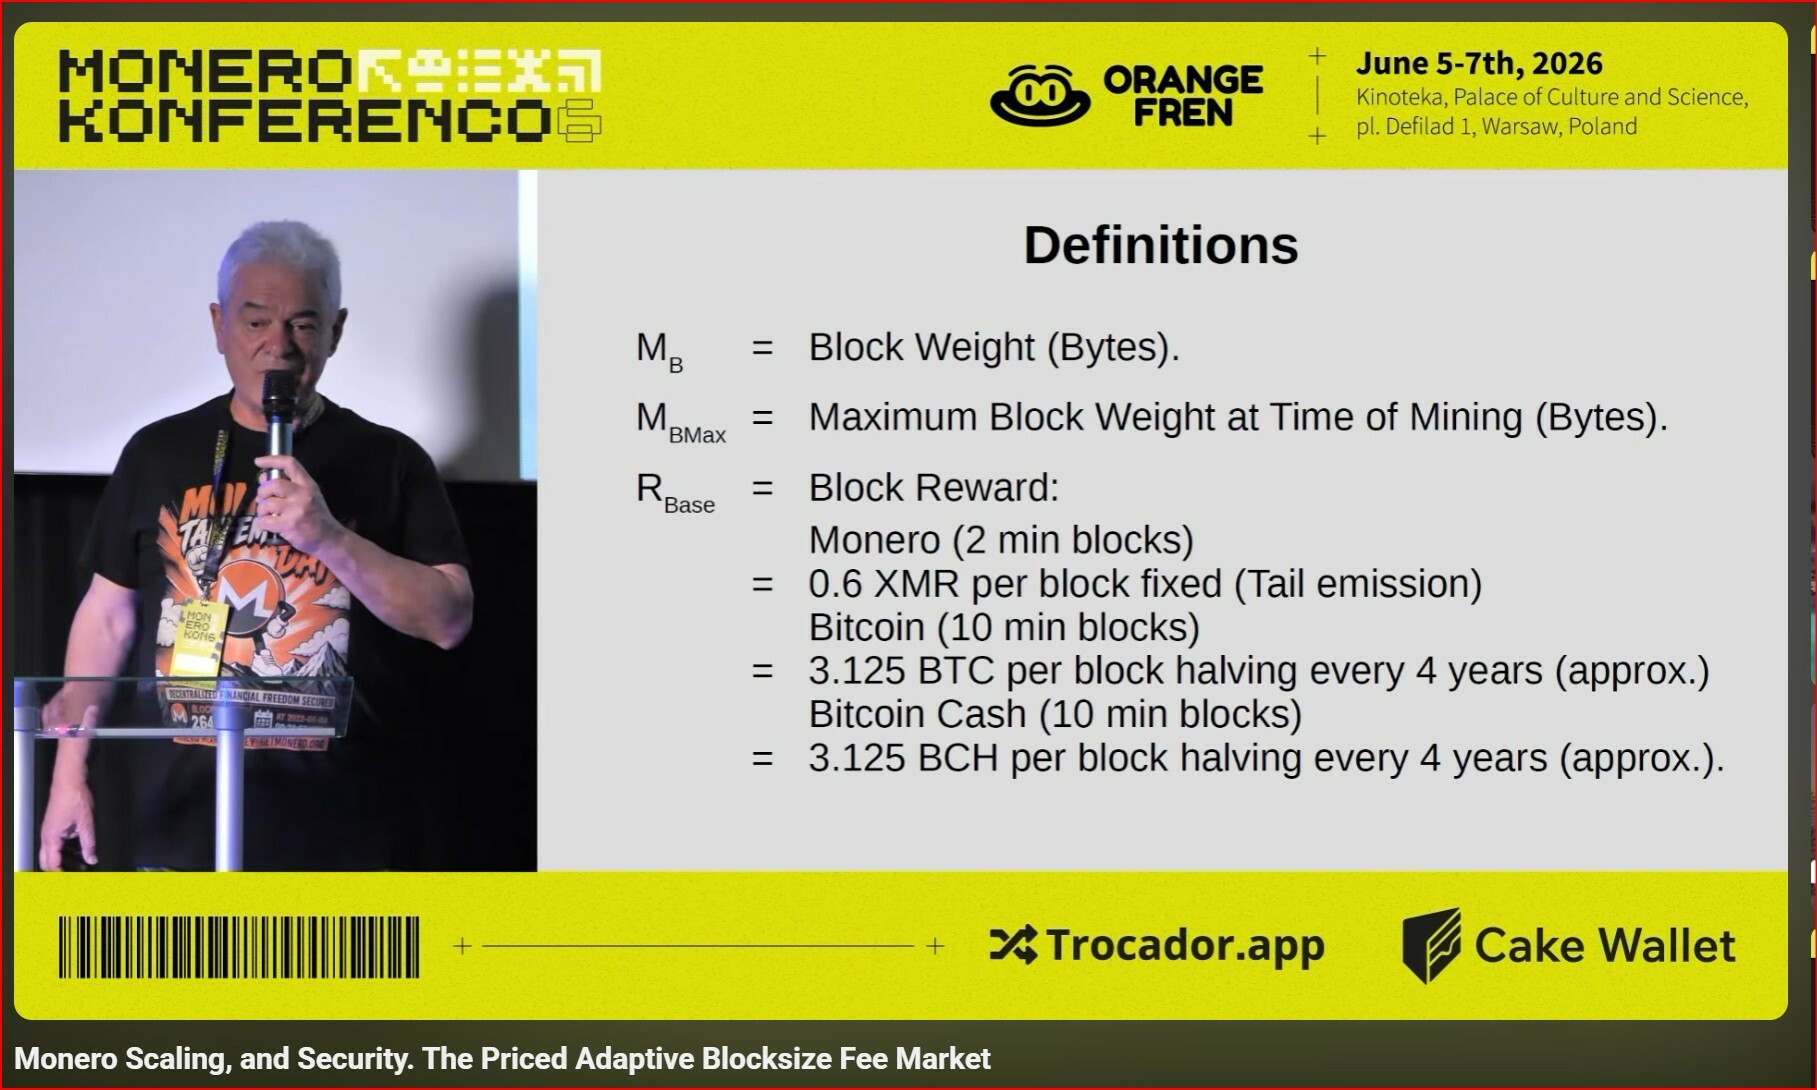
#Monero #Scaling, and #Security. The #Priced Adaptive #Blocksize #Fee_Market
NO MORE GAS THEFT;) NICE FIX Real Title. How to #COCKBLOCK_THE_THIEVES;) rotflmao Good Job!
Jun 20, 2026
Monero combines a priced adaptive block weight based upon the CryptoNote excess size penalty with a constant block reward or tail emission.of 0.6 XMR per block. This leads to a unique fee market that can provide insight into the fee markets found in Bitcoin like crypto currencies with small blocks, big blocks and adaptive blocks. We will use the the proposed Full Chain Membership Proofs++, FCMP++, Monero scaling parameters to illustrate this fee market. We will consider the inpact of pricing, and a block reward vs the lack of a block reward on this fee market. We will discuss the overall implications of different fee markets on spam mitigation, and proof of work security. We will also discuss the impact of significant transaction size and verification time increases on scalability in the light of technological change including quantum computers.
📛 DISCLAIMER: We Cover the 'Way' the #News is #COVERED_UP! 👿
#Donations (aka Operating Expenses): Coming out of 10 Years in Development, #Self_Funded.
https://www.paypal.com/donate?hosted_button_id=RQQEQPBBD69DQ
Monero XMR:
84jKr1sX6aMUSbW8bWAdnCSx2eoWze9KE94j21xooazkGtAiQCPxQBdAcouJfp2oLvD1ihaCa13uq9sKc79p6KEz57VmrS7
May you and your Family Be Blessed. Thankyou for your Consideration and Support in Advance .
Welcome to the Future of Advertising
DavidV: 25 YEARS 24/7 Experience:
* Software Architect (PhD) Supervisor -25 years 300K PMS (project management) hours
* EXPERT BLACK BOX TESTER (1999)F
* Founder of WebTafficCops.com the 1ST Dedicated CLICK FRAUD ENGINE on the Planet (1999)
* Founder of SEO (Search Engine Optimization, (1999)
* Founder of RTB (Real Time Bidding (1999)
* Founder of HFT (High Frequency Trading 2001)
* Founder of the first Screen Recorder (Applets) on the Planet (2000)
* Founder of DEVSECOPS (2000)
* Founder and CREATOR OF #BULLETPROOF #cryptocurrency FULL PRIVATE NODES via WWW since 2016 and MERCHANT INTEGRATION.
🍷 🍾 #TASTINGTRAFFIC_LLC | The Largest (WWW) #DIGITAL_TRAFFIC PROVIDER in the WORLD since 1999.
🌐 https://tastingtraffic.net/sitemap.xml
TASTINGTRAFFIC_LLC are NOT affiliates of this provider or referenced images used. This is NOT an endorsement OR Sponsored (Paid) Promotion/Reshare.
###############################
A Measurement Study on the Adoption of Pledges and Unveils in the OpenBSD Operating System https://lobste.rs/s/sglhvg #openbsd #security
https://arxiv.org/pdf/2607.03056

There was an article written recently about an rsync rewrite in Golang not being vulnerable to some vulnerabilities found in rsync.
The author went the extra mile and had some kind words to write about OpenBSD's OpenRsync as well:
https://michael.stapelberg.ch/posts/2026-05-24-minimal-memory-safe-go-rsync-vulns/#openrsync
Ironically, I saw this not long after closing a Pull Request to submit an OpenRync port to MacPorts: https://github.com/macports/macports-ports/pull/28096
Not that I don't still have an interest in such things, but it seems as if there are some other things going on (if I observed things correctly, it seems as if Apple maybe commissioned Klara Systems to port OpenRsync to macOS [e.g. https://github.com/KlaraSystems/openrsync]? Yet, it didn't seem as if they did so in a very collaborative spirit with the lead developer Kristaps Dzonsons?). Moreover, I didn't want to just leave that dangling when other MacPorts contributors were side-eyeing the PR as being left open for so long.
#OpenRsync #rsync #vulnerabilities #OpenSource #Security #Infosec #SecurityResearch #OpenBSD
The author went the extra mile and had some kind words to write about OpenBSD's OpenRsync as well:
https://michael.stapelberg.ch/posts/2026-05-24-minimal-memory-safe-go-rsync-vulns/#openrsync
Ironically, I saw this not long after closing a Pull Request to submit an OpenRync port to MacPorts: https://github.com/macports/macports-ports/pull/28096
Not that I don't still have an interest in such things, but it seems as if there are some other things going on (if I observed things correctly, it seems as if Apple maybe commissioned Klara Systems to port OpenRsync to macOS [e.g. https://github.com/KlaraSystems/openrsync]? Yet, it didn't seem as if they did so in a very collaborative spirit with the lead developer Kristaps Dzonsons?). Moreover, I didn't want to just leave that dangling when other MacPorts contributors were side-eyeing the PR as being left open for so long.
#OpenRsync #rsync #vulnerabilities #OpenSource #Security #Infosec #SecurityResearch #OpenBSD
Edited 168d ago
A Final Return for OpenBSD Anti-Return-Oriented Programming Mitigations https://lobste.rs/s/xclcel #pdf #openbsd #security
https://papers.ssrn.com/sol3/papers.cfm?abstract_id=6869668
Mark-of-the-web and pinning installers to sites https://lobste.rs/s/z4vrld #security #web
https://blog.randomoracle.io/2026/06/20/mark-of-the-web-and-pinning-installers-to-sites/

Atom Exhaustion Is Not a Footgun. It's One Third of Our CVEs via @lobsters https://lobste.rs/s/lfusbg #elixir #erlang #security
https://erlef.org/blog/security/atom-exhaustion
Forward to Hell? On Misusing Transparent DNS Forwarders For Amplification Attacks https://lobste.rs/s/ozr1zf #networking #security
https://labs.ripe.net/author/mkoch/forward-to-hell-on-misusing-transparent-dns-forwarders-for-amplification-attacks/

RE: https://mastodon.social/@_elena/116645486985827346
An #article shining light behind the #press release of a company
@_elena analyses #wsocial with exactly the right questions - " the 5 Ws of news reporting: who, what, where, when and why"
This is the kind of #journalism I am often missing these days - not just telling you what is in a companies press release but questioning everything - following the data & therefore the money
Thank you #ElenaRossini & thanks to @hannes99 for bringing it to my #attention
I'm now GNA 119 under CIRCL's GCVE system — a decentralized vulnerability
identification authority. I have authority to mint vulnerability
identifiers for cloud findings, including ones where vendor CNAs decline
to issue CVEs.
I could start assigning IDs to my own research today. I won't.
Cloud vulnerability validation shouldn't be one person's judgment. Mine
or anyone else's.
I'm forming a consensus panel of practitioners for each major cloud
platform — AWS, GCP, Azure, and managed services. GCVE-119 allocations
will go through panel review, not solo decisions.
Charter, scope, and membership criteria coming. Community input on
structure welcome before anything is finalized.
Background on GCVE and the cloud finding gap:
https://olearysec.com/gcve/
Edited 172d ago