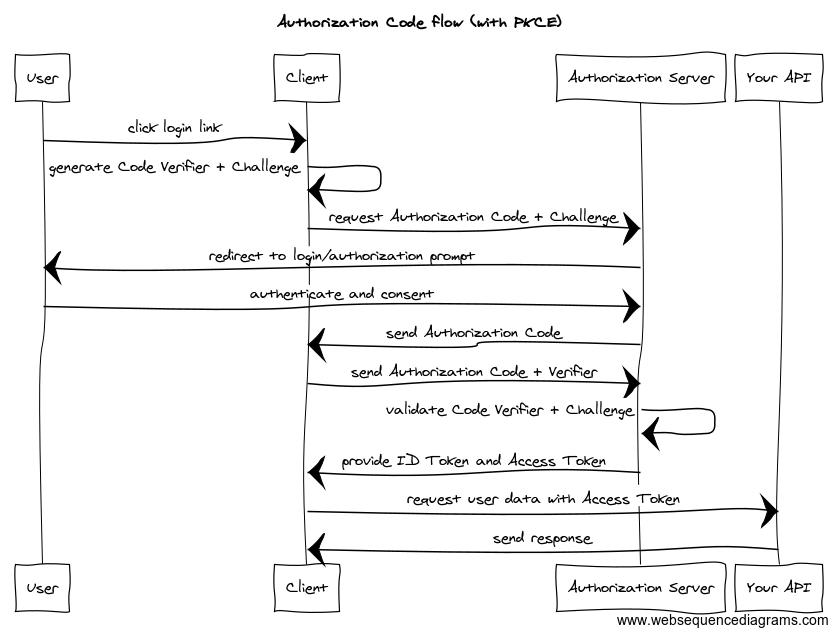
I wouldn’t say this is 100% accurate but enjoy it for what it is.. a nerdy concept explained with meme cats. 🐱
oauth

Okay, my analysis is complete! Here are the core changes to Ktistec required for Mastodon API compatibility:
- PKCE (Proof Key for Code Exchange) must be optional: Because Mastodon makes PKCE optional, clients don't support it, which means other servers can't require it. PKCE (and the
code_challengeparameter) ensures that an authorization code can only be exchanged by the client that initiated the OAuth request. - Support for the
client_credentialsgrant type: Theclient_credentialsgrant type is used to grant a client app-level access without requiring user authentication. Mastodon requires this for some of its "public" API endpoints. This necessitates a change to the database schema to allow anullaccount id in the client secrets table. - Addition of a
created_attimestamp property: Mastodon requires a non-standardcreated_atproperty in the body of the/oauth/tokenendpoint response instead of (in addition to) the standardexpires_inproperty. - Support for both form-encoded and JSON request bodies: This isn't a Mastodon requirement per se but popular clients clearly demand some latitude in what they send.
- WebFinger must accept requests with no
resourceparameter: This is honestly a bug on my part. - Mastodon-compatible endpoints: A boatload of them. Clients expect many endpoints and don't gracefully degrade if they're not present. Really I should just implement features like pinned posts and bookmarks...
The only thing here that gives me heartburn is that PKCE is not required.
Gosh this PKCE stuff goes back to 2020.
Reads:
- Dropbox: https://dropbox.tech/developers/pkce--what-and-why-
- Postman: https://blog.postman.com/pkce-oauth-how-to/
- Mastodon OAuth PKCE extension PR: https://github.com/mastodon/mastodon/pull/31129
- Mastodon OAuth documentation PR: https://github.com/mastodon/documentation/pull/1445
One of the things I'm finding stunning about the Vercel breach is how many people are saying "I had $VERY_LARGE_NUMBER of OAuth apps authorized to my $VERY_IMPORTANT_ACCOUNT and had to go through them all". I have like 2 OAuth apps authorized on any account that matters to me, and I review them fairly regularly and remove ones I don't use or don't remember. I also never accept "allow all" for any app. Apparently I'm weird in this way? I just feel like not doing this is akin to using "password" for all your passwords.
#tech #dev #security #cybersecurity #InfoSec #Vercel #breach #OAuth #AI
#tech #dev #security #cybersecurity #InfoSec #Vercel #breach #OAuth #AI
Edited 162d ago
#Hollo 0.6.0 is coming soon!
We're putting the finishing touches on our biggest security and feature update yet. Here's what's coming:
- RFC 8414 (OAuth metadata discovery)
- RFC 7636 (#PKCE support)
- Improved authorization flows following RFC 9700 best practices
New features
- Extended character limit (4K → 10K)
- Code syntax highlighting
- Customizable profile themes
- EXIF metadata stripping for privacy
Important notes for update
- Node.js 24+ required
- Updated environment variables for asset storage
- Stronger
SECRET_KEYrequirements (44+ chars)
Special thanks to @thisismissem for the extensive OAuth improvements that help keep the #fediverse secure and compatible! 🙏
Full changelog and upgrade guide coming with the release.