RE: https://eigenmagic.net/@arichtman/116583583697455397
cue Admiral Akbar’s IT’S A TRAP dot jiff
RE: https://eigenmagic.net/@arichtman/116583583697455397
cue Admiral Akbar’s IT’S A TRAP dot jiff
New by me:
Scoop: FulcrumSec Leaks Novo Nordisk Data After $25M Demand Goes Unpaid
#novonordisk #FulcrumSec #hackandleak #infosec #cybersecurity #databreach #intellectualproperty
@campuscodi @dangoodin @zackwhittaker @euroinfosec @amvinfe @briankrebs @lawrenceabrams
NEW by me:
One threat actor demanded $50 million from Novo Nordisk. Another one demanded $25 million. Neither got paid.
Two different groups tried to extort Novo Nordisk at around the same time. Novo Nordisk strung them both along, and then went dark.
Data leaks followed.
#NovoNordisk #FulcrumSec #TheUSERS007 #hackandleak #extortion #AI #databreach #infosec #cybersecurity
@campuscodi @euroinfosec @jgreig @lorenzofb @ajvicens @amvinfe
I'm now GNA 119 under CIRCL's GCVE system — a decentralized vulnerability
identification authority. I have authority to mint vulnerability
identifiers for cloud findings, including ones where vendor CNAs decline
to issue CVEs.
I could start assigning IDs to my own research today. I won't.
Cloud vulnerability validation shouldn't be one person's judgment. Mine
or anyone else's.
I'm forming a consensus panel of practitioners for each major cloud
platform — AWS, GCP, Azure, and managed services. GCVE-119 allocations
will go through panel review, not solo decisions.
Charter, scope, and membership criteria coming. Community input on
structure welcome before anything is finalized.
Background on GCVE and the cloud finding gap:
https://olearysec.com/gcve/
New methodology paper: The Calculator Discipline.
A four-class taxonomy of AI-assisted disclosure hallucinations, a pre-send filter that catches the mechanical ones, and two real withdrawals from my own OpenBSD work — including the one Theo de Raadt asked the right question about.
Honest case studies from the sender's end of a problem the field has only described from the receiving end.
DOI: 10.5281/zenodo.20393083
Read: https://stuart-thomas.com/research/calculator-discipline/
The Great American State Fair cancellations are getting framed as a culture war story. Stop there. The real signal worth tracking is what happens to event infrastructure when organizers face coordinated pressure campaigns online.
Large public gatherings tied to...
Read more: https://steelefortress.com/i10igu
Security #Cybersecurity #ThreatIntel #InfoSec
New blog post!
This time I talk about my new favorite evasive shellcode loader, Charon. I give a brief overview about what it does, how it works and which techniques it uses.
Also a brief addendum for enjoyers of bloated Implants such as Sliver.
https://ti-kallisti.com/general/ms/descending-into-hades.html
#InfoSec #Malware #Shellcode #RedTeam #RedTeaming #Pentesting #Charon #Sliver #Merlin #Mythic
So, one of my resolutions this year was to write more code.
I love to break stuff, but last year I reignited my passion for coding and I would really love to contribute to the community that has given me so much and continues to do so.
And contributing works a lot better by creating, rather than breaking.
So I created a codeberg account. And I already have a first repo published!
I called it Axmar.
Axmar is a C# implementation of the SilentHarvest technique that was published last year.
It uses backup access and rarely used APIs to (mostly) stealthily read the local credentials database in Windows system.
Enjoy!
https://codeberg.org/Ti-Kallisti/Axmar
#foss #coding #infosec #malware #pentesting #redteaming #codeberg #windows #csharp
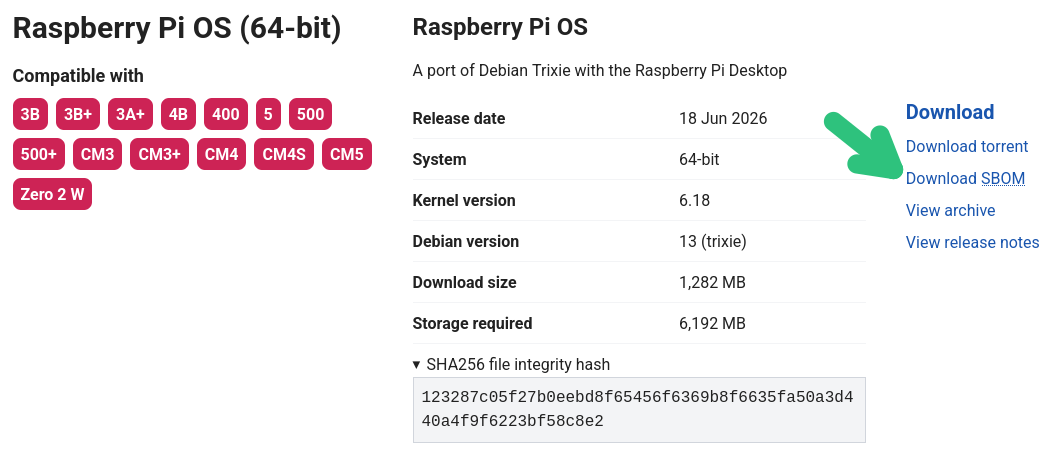
Raspberry Pi now publishes a Software Bill Of Materials (SBOM) with each PiOS download
and a torrent
and a link to the release notes
and a link to the release archive
and the release date
and a checksum
and the download and install storage sizes
and the architecture, kernel, and upstream release versions
and a list of all compatible hardware
in the same place.
https://www.raspberrypi.com/software/operating-systems/
How is your Enterprise software vendor doing?
#RaspberryPi #PiOS #SBOM #SoftwareBillOfMaterials #InfoSec #InformationSecurity #CyberSecurity
⋅ Microsoft under fire for threatening security researcher with criminal investigation
RE: https://cyberplace.social/@GossiTheDog/116676826944489315
I need people to understand that stuff like this will keep happening, for two reasons:
1. To be useful these chatbots need to have full access to everything they are supposed to "manage"; otherwise they are pointless.
2. Trying to stop prompt injection is basically trying to semantically filter natural language.
These tools have no model of the world, no ontology to anchor any "safety instructions" in. There will always be a way to talk one's way around them.
CVSS 10.0 in Google Config Connector — still unpatched.
Any K8s namespace user can become GCP Org Owner with 3 lines of YAML. Google's engineer said "Nice catch!" Then VRP called it "working as intended."
Their defense contradicts their own documentation.
Full writeup + video PoC: https://olearysec.com/research/config-connector-authorization-bypass
#infosec #cloudsecurity #gcp #kubernetes #bugbounty #vulnerability #google #k8s #iam #cybersecurity
"Your database has been exposed in a third-party breach."
You wouldn't have to worry about your desktop settings, search history, or app preferences leaking in a corporate data breach if those companies didn't insist on syncing them to their servers in the first place. The only good thing is that Facebook is giving you money
#lucentOS is built on a zero-telemetry baseline. What happens on your desktop stays on your desktop.
https://github.com/dixon-team-tech/lucentOS
#Infosec #Cybersecurity #PrivacyMatters
RE: https://infosec.exchange/@mttaggart/116830015225440372
This is a really important read for understanding both what's under the hood with LLMs, but also why it is impossible to secure any #LLM.
In the thread, I posted a couple of extra links to experts explaining that last sentence better than I can. But read the article Taggart linked first.
Hey, can I get some legal experts in here to tell me I’m wrong about what I think this ruling means? Also, how does international case precedence work?
A #German court has ruled that Google is directly liable for what its #AI #search overviews say. Previous case law shielding search engine operators from liability doesn't apply to AI overviews.
That’s freaking massive. Google’s AI responses are wrong almost 10% of the time, make up sources, and infer facts not in evidence, and cause real harm. Germany says publisher immunity does not convey when the company product, the ai, is stating things as fact.
Losing publisher #immunity is a really, really big deal. Especially if we can get a similar ruling in the US, and if this ruling flows into EU precedent.(I don’t know how any of that works)
In any case, go German law writers.
#infosec #truthiness #llm https://the-decoder.com/landmark-german-ruling-declares-googles-ai-overviews-are-googles-own-words-and-makes-it-liable-for-false-answers/
Arthur C. Clarke: "Any sufficiently advanced technology is indistinguishable from magic."
Me: "Therefore, any sufficiently complicated technical problem is indistinguishable from a curse."
#Github Security Advisories program is struggling under the load of new submissions. Delays in CVE assignment up to a month are being reported. Apparently, May 2026 was the highest volume month ever, and they are working through a backlog.
source: https://www.openwall.com/lists/oss-security/2026/06/10/9
It is not very hard to figure out what is going on: The amount of AI-assisted reports is flooding the systems. Considering the asymmetric nature of the situation (limited human resources processing increasing number of reports), it is unlikely the it is getting any better soon.
If just tracking and assigning issues is getting this hard, it can't bode well for actually fixing and patching them.
✨ A sparkle icon appears in an app that no one in IT approved. The help desk can't explain it, and it's already processing your data! This kept coming up in conversations with other CIOs, so I wrote about it in my latest Forbes piece.
The pattern repeats across so many vendors; here are just a few:
・Zoom auto-enabled AI Companion on host accounts, with recordings and full transcripts already defaulted on
・Microsoft 365 Copilot activates for every admin if your tenant holds a single paid license, and opting out means building a special security group
・Google's Workspace Intelligence shipped default-on for Gmail, Drive, Chat, and Calendar, with admin controls lagging the live feature by up to 72 hours
・OpenAI disables connectors by default for Enterprise customers but enables them for Business. Same vendor, opposite defaults.
Every default-on feature just transfers governance work from the vendor to you, along with wiretap exposure and e-discovery sprawl that nobody signed up for.
My ask of vendors is simple: ship AI features off by default and give admins an evaluation window measured in weeks, not days. Until that happens, assume the next AI feature is already live in your tenant. Review your configurations like it's a recurring operational task, because it is.
Full piece here: https://www.forbes.com/councils/forbestechcouncil/2026/06/10/default-on-ai-are-saas-vendors-outsourcing-their-risk-to-you
#RiskManagement #Forbes #ForbesTechnologyCouncil #ForbesTechCouncil #leadership #security #privacy #cloud #infosec #cybersecurity #AI #SaaS
@forbes @Forbes@newsie.social @forbestechcncl @RHR_International @depaulu #DePaul #DepaulU #DePaulUniversity #DePaulCDM




 🎸 🏳️🌈 ⁂