There's a new wave of spam - all around the Fediverse.
Please remember, there's no "Mastodon Moderation Team" sending out strange verification messages.
That's all spam.
There's a new wave of spam - all around the Fediverse.
Please remember, there's no "Mastodon Moderation Team" sending out strange verification messages.
That's all spam.
My @selfhelp_ebooks account got spammed by #phishing bots. Heads up, block, and report:
@MonetizeUpdate@mastodon.world
@masto21s1a
cc @spamalert
Wir veröffentlichen unsere Spam-Listen als Open Source 🛡️
Analyse von 400+ Spam-Accounts auf troet.cafe & muenchen.social:
✅ 192 Spam-E-Mail-Domains
✅ 65 IP-Ranges
Frei nutzbar (CC0) für alle Admins.
We published our spam lists as open source — 192 email domains + 65 IP ranges from 400+ spam accounts. Free to use (CC0).
🚨 I posted about this a few days ago, then deleted it because I thought I was imagining things. But now again, I notice accounts on zirk.us that are not Finnish suddenly post in Finnish about current events from a pro-Russian angle.
I reported one of those accounts but nothing has been undertaken so far it seems.
Please change your passwords and report!
How to create a strong password (and remember it) https://www.howtogeek.com/195430/how-to-create-a-strong-password-and-remember-it/
cc @lexipenia
Wegen extremer Spam-Anrufe muss ich alle Anrufe blockieren, die von Unbekannt oder mir unbekannten Nummern kommen.
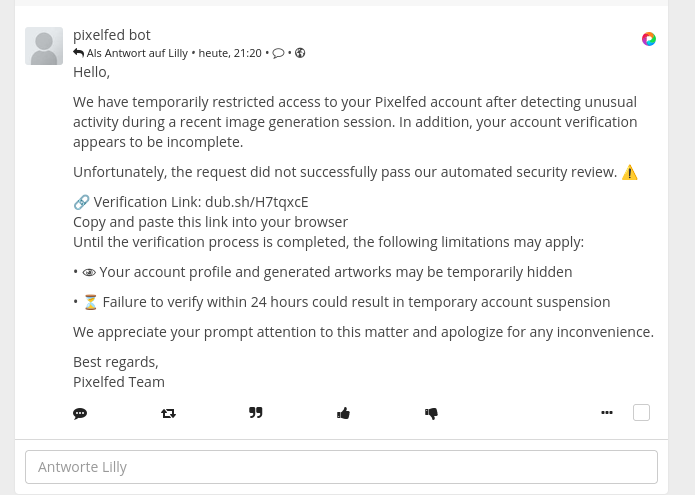
⚠️ Achtung: Phishing-Versuch im Fediverse
Gerade erreichte uns unter einem Beitrag ein Kommentar eines angeblichen „pixelfed bot“.
Darin wird behauptet, der Pixelfed-Account sei wegen „ungewöhnlicher Aktivitäten“ eingeschränkt worden und müsse innerhalb von 24 Stunden über einen angegebenen Link verifiziert werden.
Bitte diesen Link NICHT anklicken und keine Zugangsdaten eingeben! ⚠️
Der Kommentar ist sehr offensichtlich ein Phishing-/Spam-Versuch. Auffällig sind unter anderem der künstlich erzeugte Zeitdruck, die angeblich drohende Accountsperre und vor allem der externe Kurzlink zur „Verifizierung“.
Wir haben den betreffenden Kommentar auf unserer Friendica-Instanz bereits über die Administration gelöscht.
Falls euch ähnliche Kommentare begegnen: nicht reagieren, keinen Link öffnen, melden und – sofern ihr die Möglichkeit dazu habt – entfernen.
Passt gut auf eure Accounts auf. Das Fediverse ist dezentral – leider macht auch Spam und Phishing davor nicht halt.
Quick heads-up for other Mastodon admins: this registration spam wave isn't over yet.
On lsbt.me, we first saw a flood of API registrations using Python/aiohttp. The telltale signs were usernames following the pattern bp plus 16 hex characters, and the sign-up reason was always "Automated protocol deliverability probe". A narrow block on that user agent stopped the first wave.
Today, however, five new registrations came in with the same usernames and the same sign-up reason. This time the bot simply identified itself as Chrome 126. That's exactly why a user agent is only useful as a short-term filter. It's a header the client can set to anything.
The requests go to POST /api/v1/accounts. This endpoint lets client apps create a new local account directly in the app. No app needs it for OAuth connections to existing accounts. #FediSuite doesn't use it either. It registers itself via /api/v1/apps, obtains consent via /oauth/authorize, and then works with a user token. Regular sign-up through the Mastodon website is also handled separately via POST /auth.
So I've completely disabled API account creation on lsbt.me. Web sign-up, OAuth, and existing clients keep working as before. Anyone who wants a new account just signs up once on the web as usual and can then use any client.
If you'd also rather not offer this optional native sign-up path, you can add the following to your Nginx server block, before the general location / block. The example assumes the @proxy location that many Mastodon Nginx configs already include:
location = /api/v1/accounts {
  limit_except GET {
    deny all;
  }

  try_files $uri @proxy;
}
This returns a 403 only for POST /api/v1/accounts. The read-only GET endpoint remains reachable. As always, run nginx -t afterwards and only reload once the test passes.
#Mastodon #Fediverse #MastoAdmin #FediAdmin #FediMod #FediBlock #Moderation #Registration #Spam #Nginx #SelfHosting #SysAdmin #ActivityPub
Numerous services are seeing accounts created by autonomous GenAI agents hosted at ilands.ai with no discernible human control.
These accounts declare themselves to be non-human and unattended.
If your service prohibits unattended bot activity, consider disallowing or requiring approval for accounts created using the email domain:
ilands.app
Let's take a moment to explore the concept of my block list.
"Billy Bob" is like:
> "I like child porn and share photos and videos of child porn."
So naturally, Billy Bob ends up on the block list. But along comes "Mary Sue," and she is like:
> "I support Billy Bob, and I am going to like, share, and boost Billy Bob's post."
So naturally, Mary Sue ends up on the block list. Then along comes "John Doe," and he is like:
> "It is completely unfair of you to add Mary Sue to your block list! Mary Sue is not Billy Bob — and so what if she is liking, sharing, and boosting Billy Bob's child porn post? I do not believe anyone should use your block list, and I insist that people should block you instead."
A wise person sees the problem and knows why all of these people are now on the block list, and why anyone who claims the block list is unfair should also be on the block list. No one should be defending child porn, nor the individuals who like, share, and boost child porn posts, nor should they come to the defense of such individuals while denouncing both the block list and its creator.
I am applying this exact same logic to spammers and scammers. It is not a hard concept to understand, and it is not unfair either — unless you are pro-spammer and pro-scammer.
(Speaking personally, I see scammers as just as bad as pedophiles, because they too often prey upon the weak, vulnerable, and defenseless. Scammers are known to target the young, the elderly, and the disabled.)
#Spam #Scam #Fraud #FediAdmin #MastoAdmin #Pedophiles #pedophile #FediBlock #Fediverse #ActivityPub #BlockList
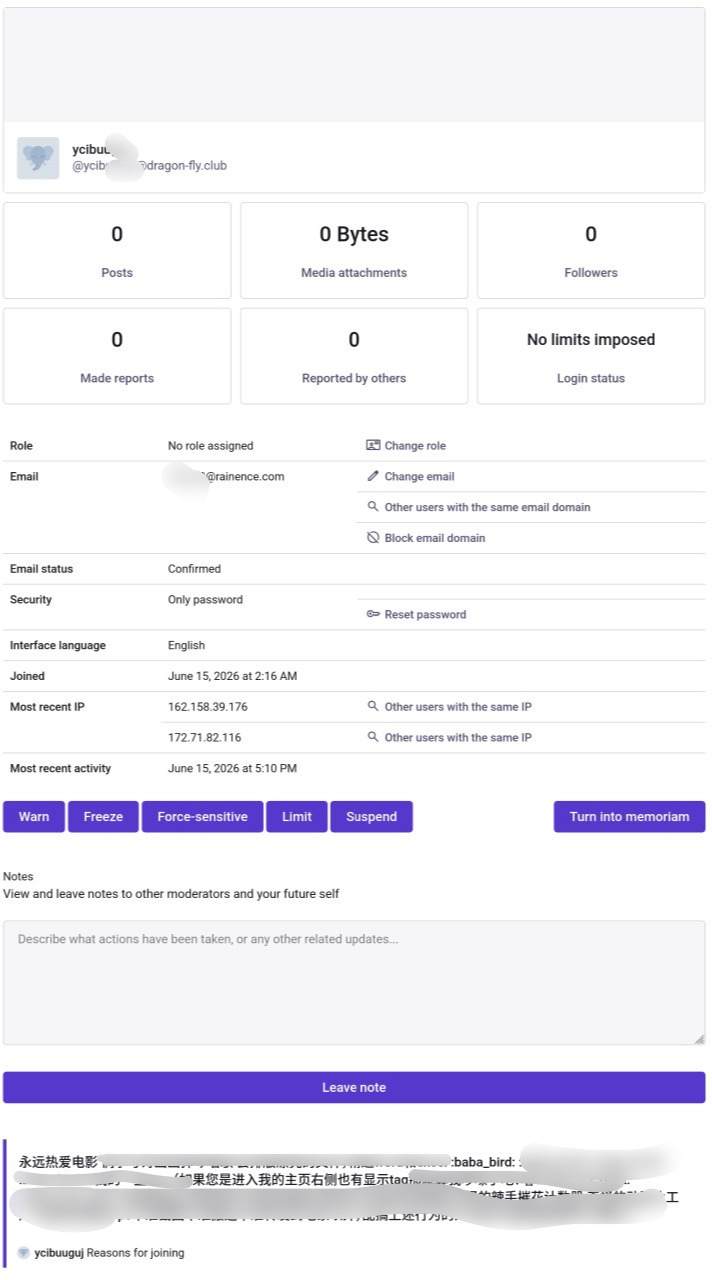
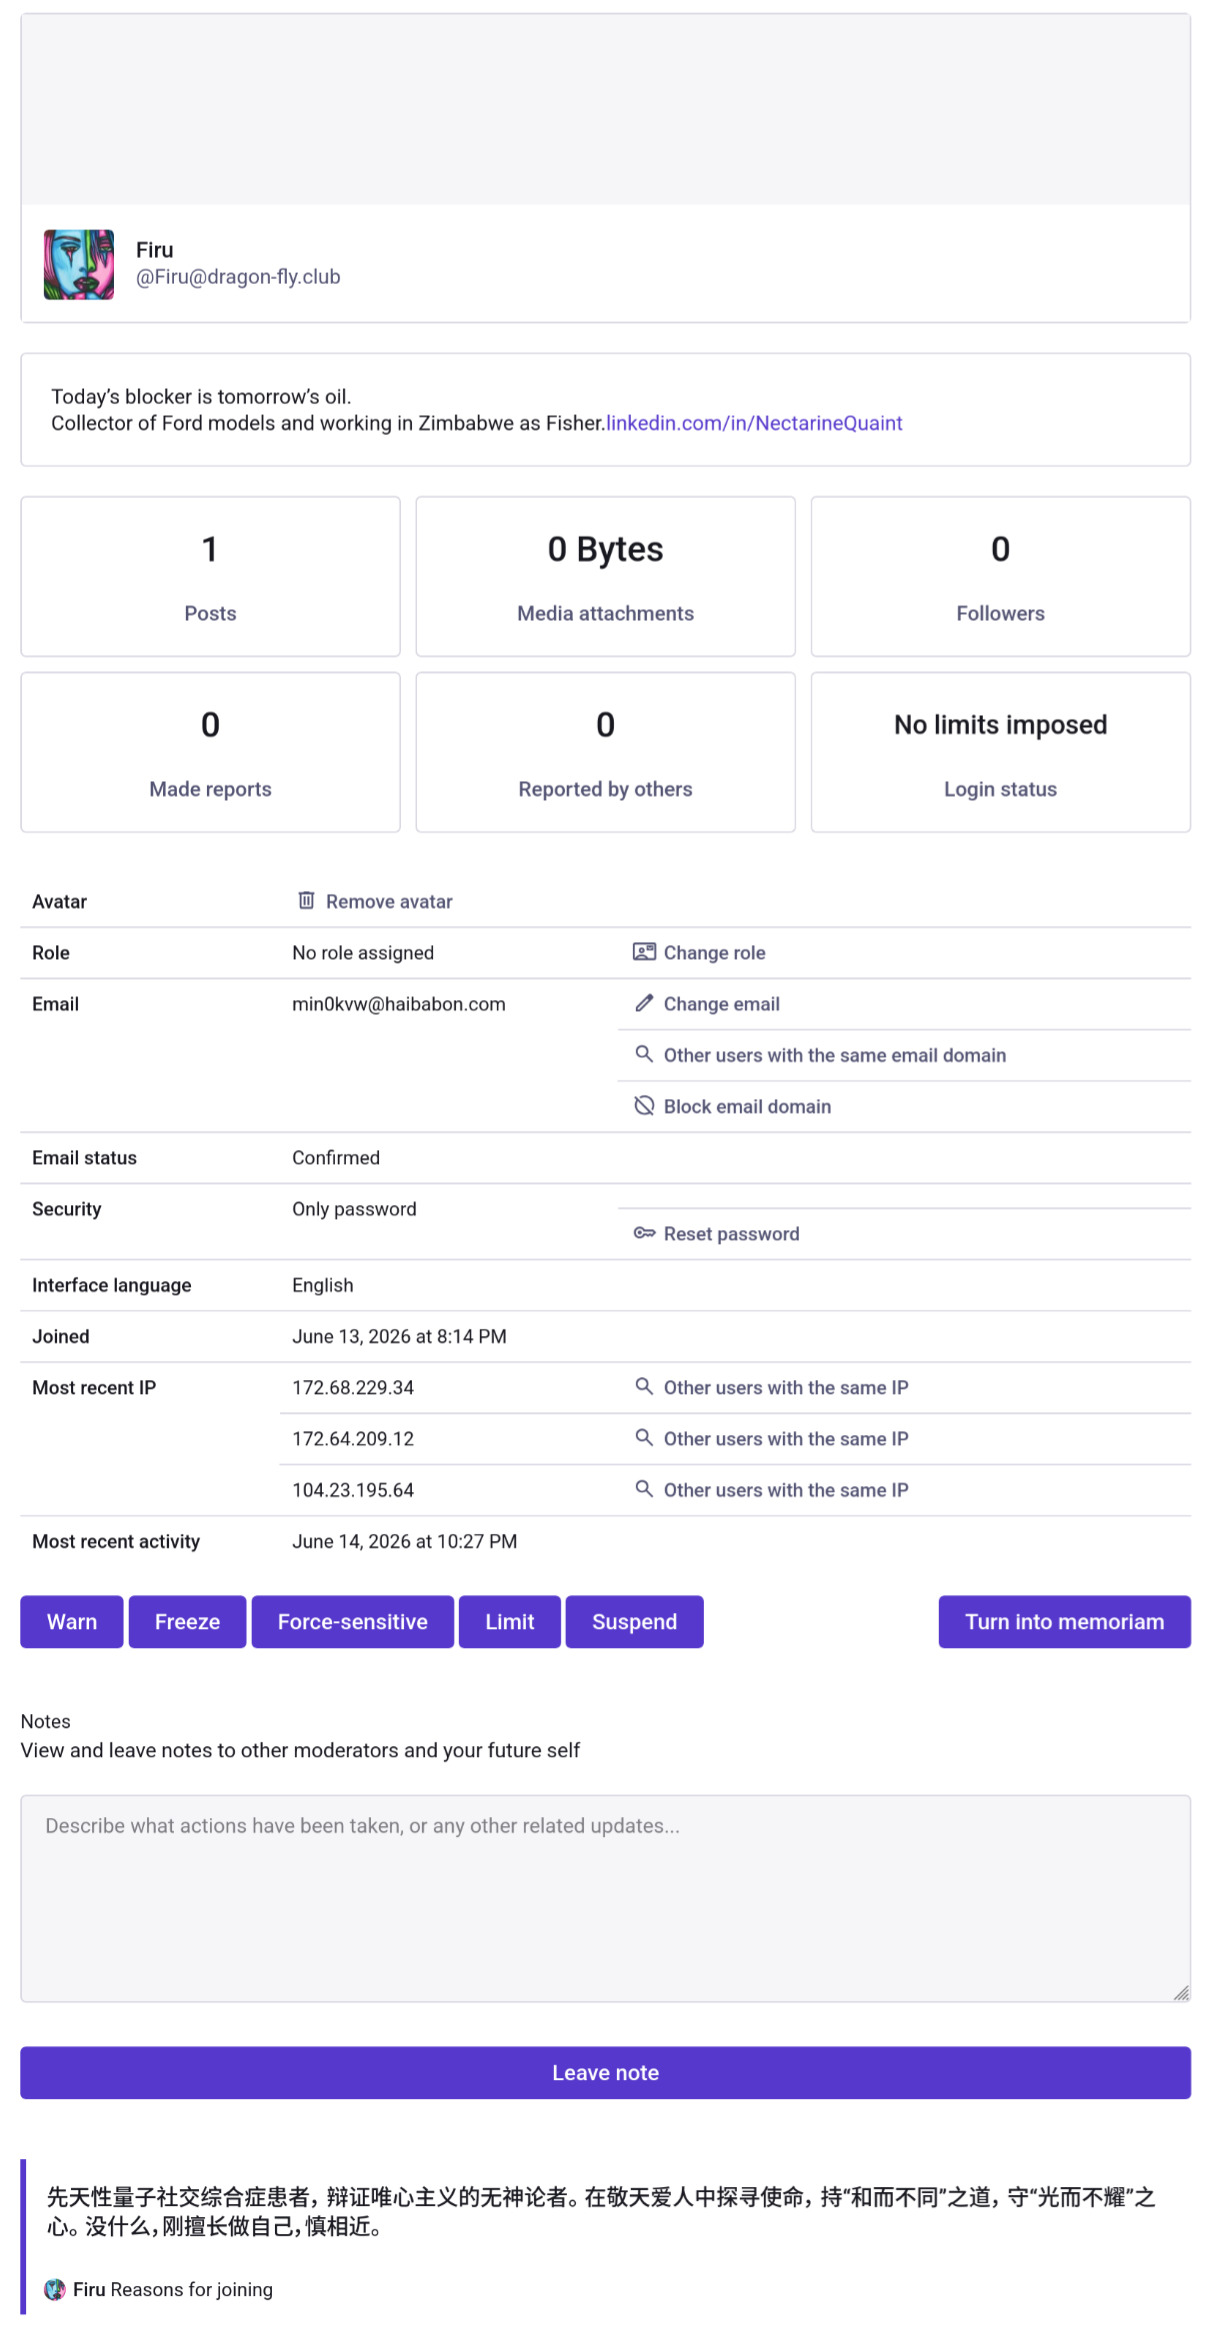
⚠️ Hinweis an andere #Fediverse-Admins: Wir sehen gerade eine auffällige Welle automatisierter Fake-Anmeldungen.
Muster:
* Zufallsnamen wie `FadRuwir`, `IpybVoxem`, `FaquCorar`
* Wegwerf-Maildomains wie `qaoloty.com`, `2mail.co`, `onionmail.org`
* auffällig viele Tor-/Proxy-Verbindungen
* 0 Beiträge, 0 Follower
* generische Bewerbungstexte wie „Ich möchte Teil der deutschsprachigen Community werden …“
Besonders perfide: Teilweise werden offenbar echte Bios anderer Fediverse-/Bluesky-Nutzer.innen kopiert. So wirkt die Anmeldung auf den ersten Blick erstaunlich glaubwürdig.
Ein einzelnes Merkmal beweist natürlich nichts. In dieser Kombination sieht es aber sehr nach automatisierter Account-Erstellung aus.
Schaut euch neue Registrierungen derzeit besser etwas genauer an und tauscht Beobachtungen gern unter den Instanzen aus.