This week's net.wars, "The Sutton effect", goes to the 25th Workshop on the Economics of Information Security, where researchers mull the costs of cybersecurity failures: https://netwars.pelicancrossing.net/2026/06/05/the-sutton-effect/ #NetWars #security #economics
security
Creating a development sandbox with crosvm https://lobste.rs/s/mml3sh #practices #security #virtualization
https://www.erat.org/crosvm.html
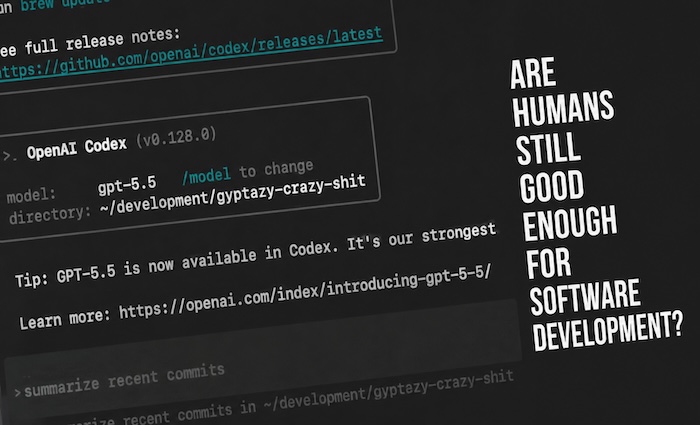
AI assisted pen testing, coding and arising secvulns. Are we humans still good enough?
the last weeks we saw more and more security issues coming up. Let's talk!
Sorry, a pretty long blog post about this...
https://gyptazy.com/blog/coding-after-ai-are-humans-still-good-enough/
#ai #aicoding #coding #opensource #foss #security #infosec #vulns #developer #devops #engineer #ops #fedi #philosophy
the last weeks we saw more and more security issues coming up. Let's talk!
Sorry, a pretty long blog post about this...
https://gyptazy.com/blog/coding-after-ai-are-humans-still-good-enough/
#ai #aicoding #coding #opensource #foss #security #infosec #vulns #developer #devops #engineer #ops #fedi #philosophy
Edited 178d ago
Open Source as Infrastructure: Taking Roads and Bridges literally via @robey https://lobste.rs/s/z2wzap #security #testing
https://nesbitt.io/2026/06/30/taking-roads-and-bridges-literally.html
Integrity on Embedded Linux Devices under the Cyber Resilience Act https://lobste.rs/s/ypba4x #linux #security
https://sigma-star.at/blog/2026/06/integrity-on-embedded-linux-devices-under-the-cyber-resilience-act/
Autocrypt v2 - Post-Quantum and Reliable Deletion https://lobste.rs/s/esy9xh #cryptography #security
https://autocrypt2.org
Vulnerability and malware checks in uv by @yossarian https://lobste.rs/s/mct5rz #python #security
https://astral.sh/blog/uv-audit
Expanding Private Cloud Compute - Apple Security Research https://lobste.rs/s/4xbzbk #ai #privacy #security
https://security.apple.com/blog/expanding-pcc/
Self-hosting email the hard way from your own routable IPv4 block up https://lobste.rs/s/cw7vxa #ml #networking #security
https://anil.recoil.org/notes/recoil-self-hosting-2026
Arbitrary code execution in objdump -g https://lobste.rs/s/sbcasc #security
https://blog.calif.io/p/oobdump-relocation-oriented-programming
For the 2nd time in weeks, Microsoft packages laced with credential stealer https://lobste.rs/s/ryxjww #security
https://arstechnica.com/security/2026/06/for-the-2nd-time-in-weeks-microsoft-packages-laced-with-credential-stealer/
Longinus: 2 Boundaries in One Bug, Piercing Chrome’s Renderer and V8 Sandbox with a Single Vulnerability, CVE-2026-6307 https://lobste.rs/s/uaoe9y #security #web
https://nebusec.ai/research/v8-cve-2026-6307-writeup/
Do excellent vulnerability reports via @andrewnez https://lobste.rs/s/pwr4h7 #security
https://daniel.haxx.se/blog/2026/06/29/do-excellent-vulnerability-reports/
ipv6_frag_escape: Linux LPE - Reliable Jail/Container Escape https://lobste.rs/s/eihlve #devops #security
https://github.com/sgkdev/ipv6_frag_escape
pomerium: Pomerium is an identity and context-aware access proxy https://lobste.rs/s/9mtucy #networking #security #web
https://github.com/pomerium/pomerium
Unprivileged root via a use-after-free in DRM GEM change_handle (CVE-2026-46215) https://lobste.rs/s/hh5yyq #linux #security
https://cyberstan.co.uk/drm-lpe-linux/
Old Wine in a New Bottle: A Decade-Old lxd-Group Root, Re-Armed https://lobste.rs/s/xuusc9 #linux #security
https://starlabs.sg/blog/2026/06-old-wine-in-a-new-bottle-a-decade-old-lxd-group-root-re-armed/
We have to change the rules of security https://lobste.rs/s/ku6lzl #practices #security
https://opensourcesecurity.io/2026/06-rules-of-security/
The FCC wants to make it impossible to buy "burner" phones, such as pre-paid phones not linked to your identity. They plan to do this by forcing all companies to store a ton of data about ALL phone users, including Copy of ID, and Verified address and a ton more info for both new & existing phone users, regardless of company or phone.
CVE-2026-45447: Heap Use-After-Free in the PKCS7_verify() Function https://lobste.rs/s/yg1xb2 #security
https://openssl-library.org/news/vulnerabilities/#CVE-2026-45447
Building a passive Ethernet tap https://lobste.rs/s/qwk5vn #hardware #networking #security
https://blog.lvmbdv.dev/posts/building-a-passive-ethernet-tap/
Off By !: Exploiting a Use-after-Free in the Linux Kernel https://lobste.rs/s/mnfcv4 #linux #security
https://blog.exodusintel.com/2026/06/08/off-by-exploiting-a-use-after-free-in-the-linux-kernel/
17 bugs in 10 weeks from AI security scanning https://lobste.rs/s/5iuaxt #security #vibecoding
https://lalitm.com/post/perfetto-security-bugs-ai/
Trojaned OpenSSH (in 2002) https://lobste.rs/s/ti42hu #openbsd #security
http://miod.online.fr/software/openbsd/stories/trojan.html
Preventing token theft https://lobste.rs/s/agwtde #security
https://codon.org.uk/~mjg59/blog/p/preventing-token-theft/